Beschrijving
oopspam is a modern anti-spam solution that uses advanced AI and machine learning to protect your WordPress forms and comments from spam. Our system has blocked over 1 billion spam attempts across 3.5M+ websites, maintaining 99.9% accuracy without compromising user privacy or accessibility.
Unlike traditional CAPTCHA solutions that can hurt your conversion rates, oopspam works silently in the background, analyzing submissions against our extensive database of 500M+ malicious IPs and emails to catch both bot and human spammers.
Why Choose oopspam?
- Bescherm formulieren zonder CAPTCHA, JavaScript uitdagingen of het volgen van bezoekers.
- Vang spam van bots en van mensen met AI-analyse en contextuele controles.
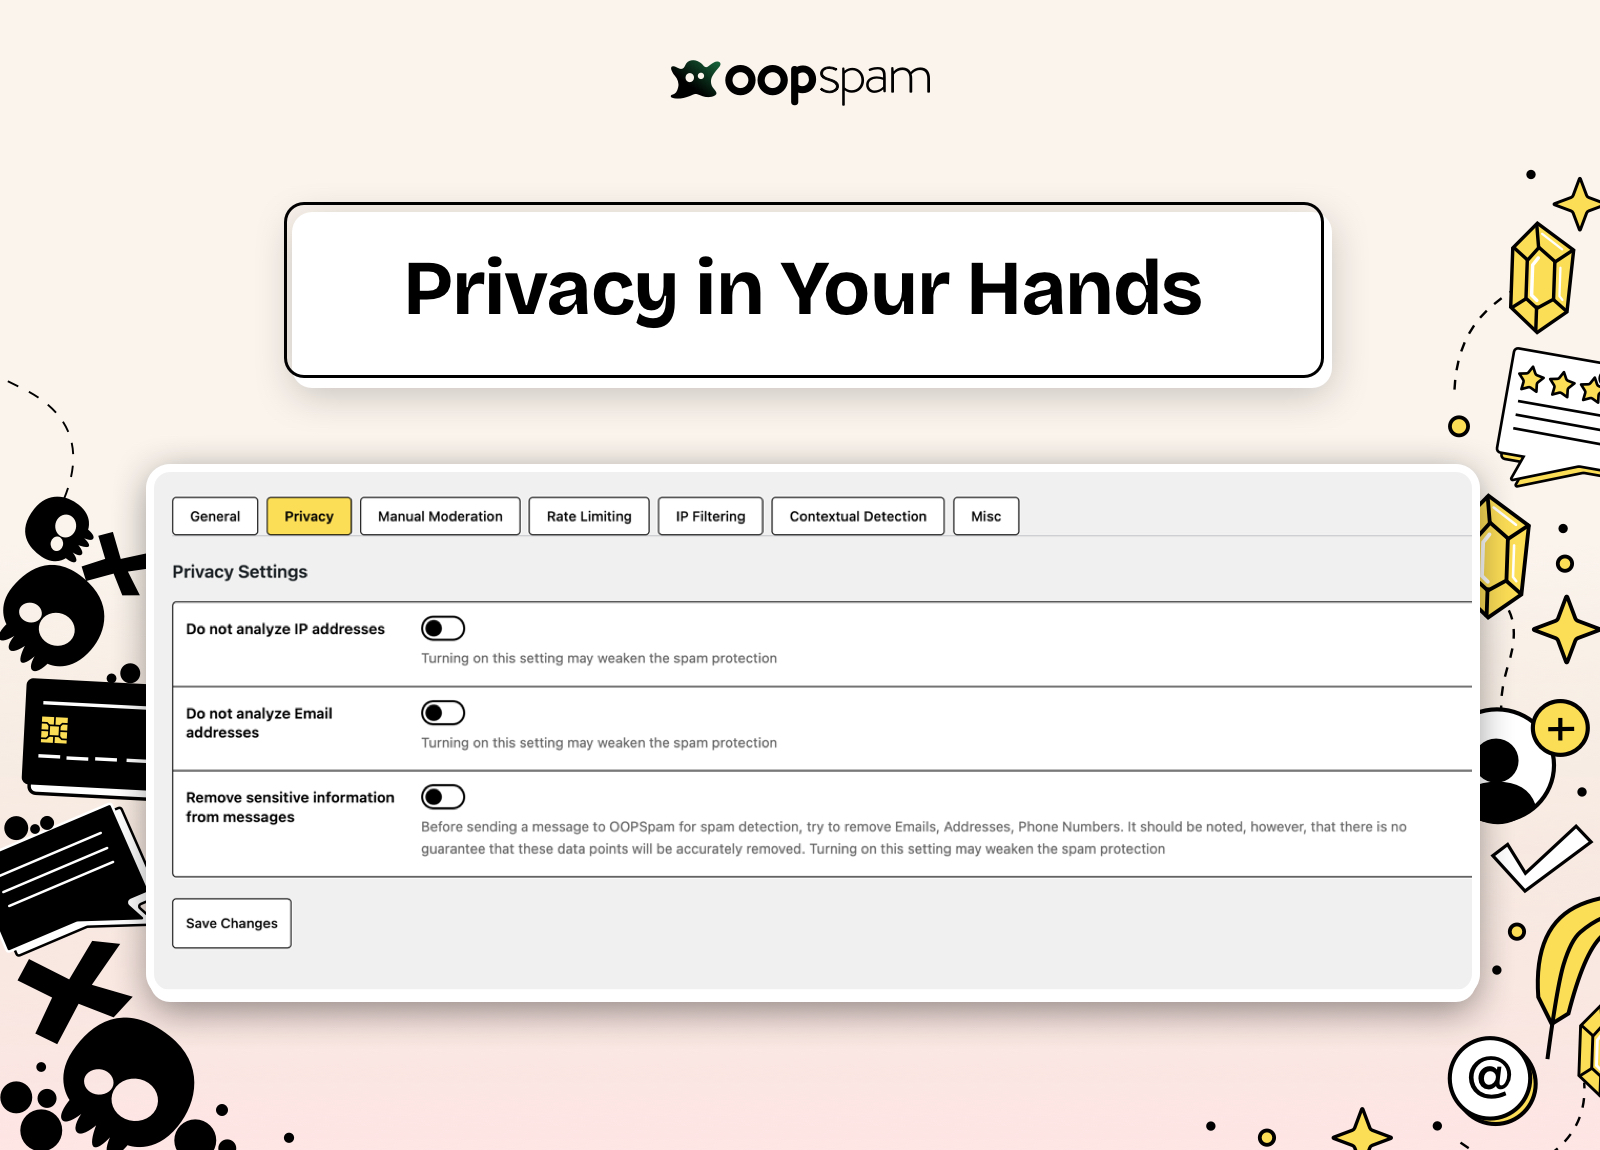
- Houd controle over je privacy met optionele IP- en e-mailanalyse, waarbij de logs in je WordPress-database worden opgeslagen.
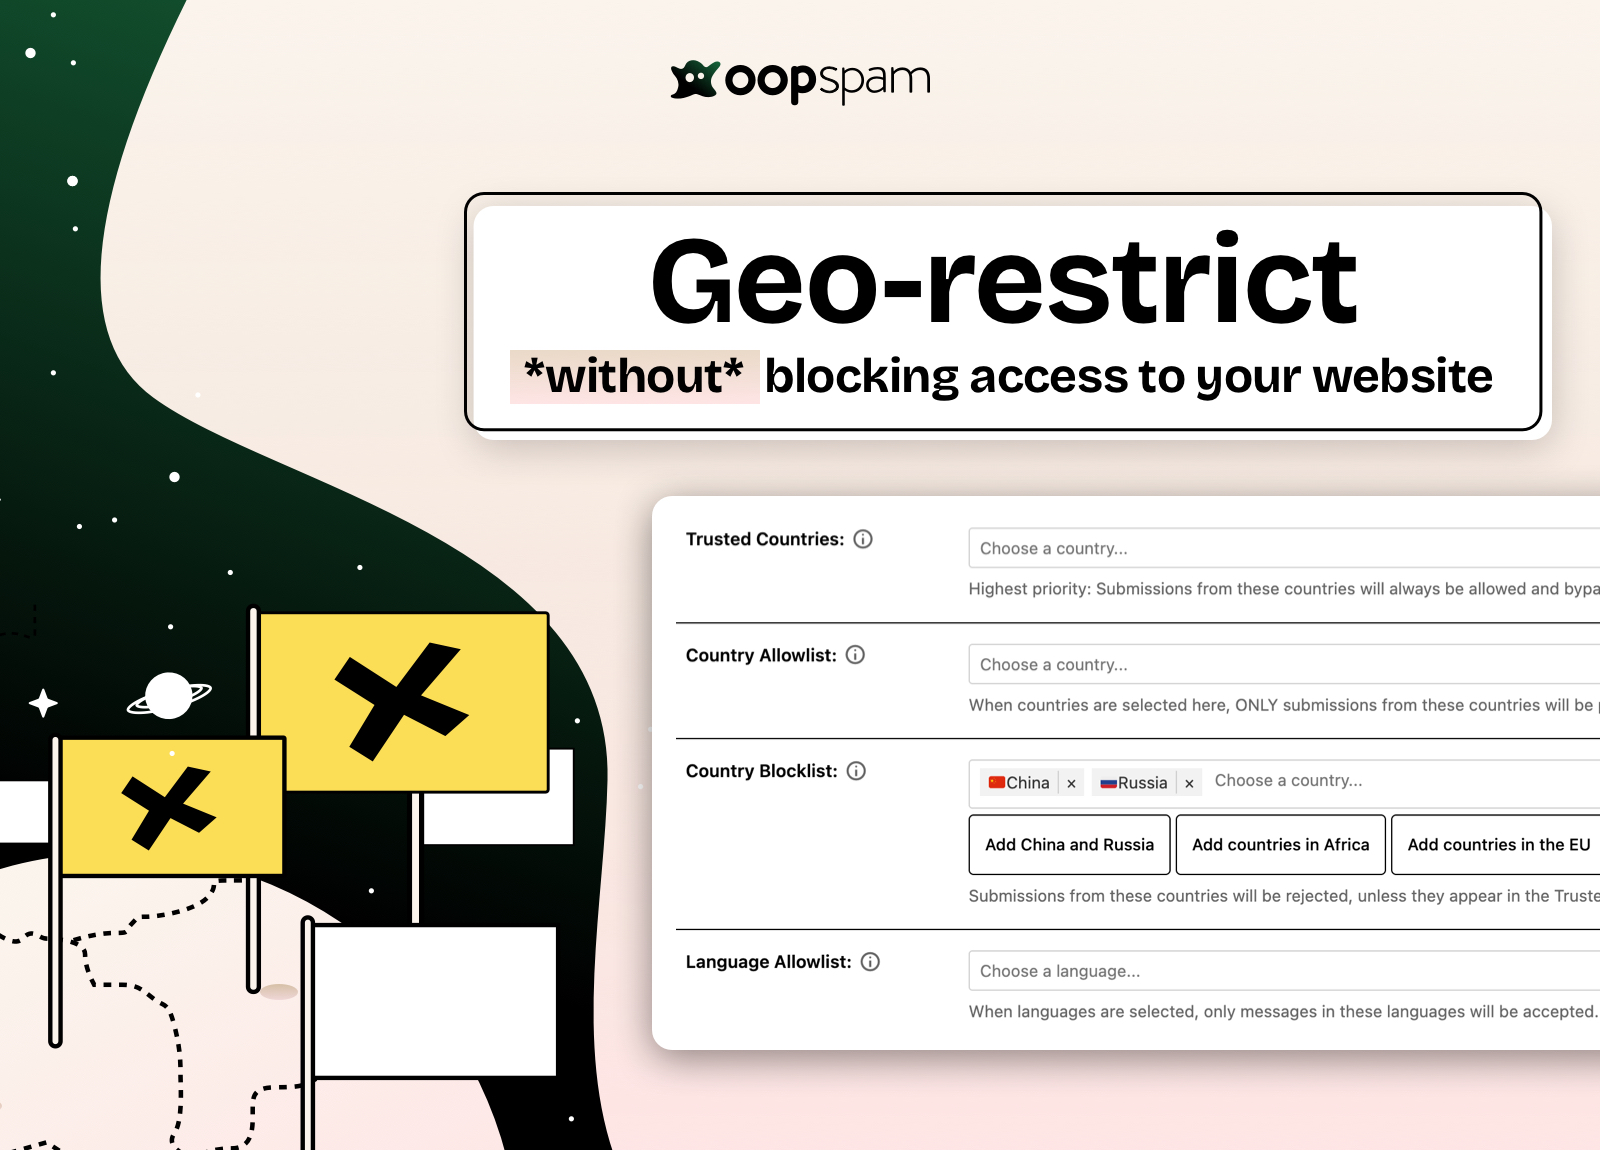
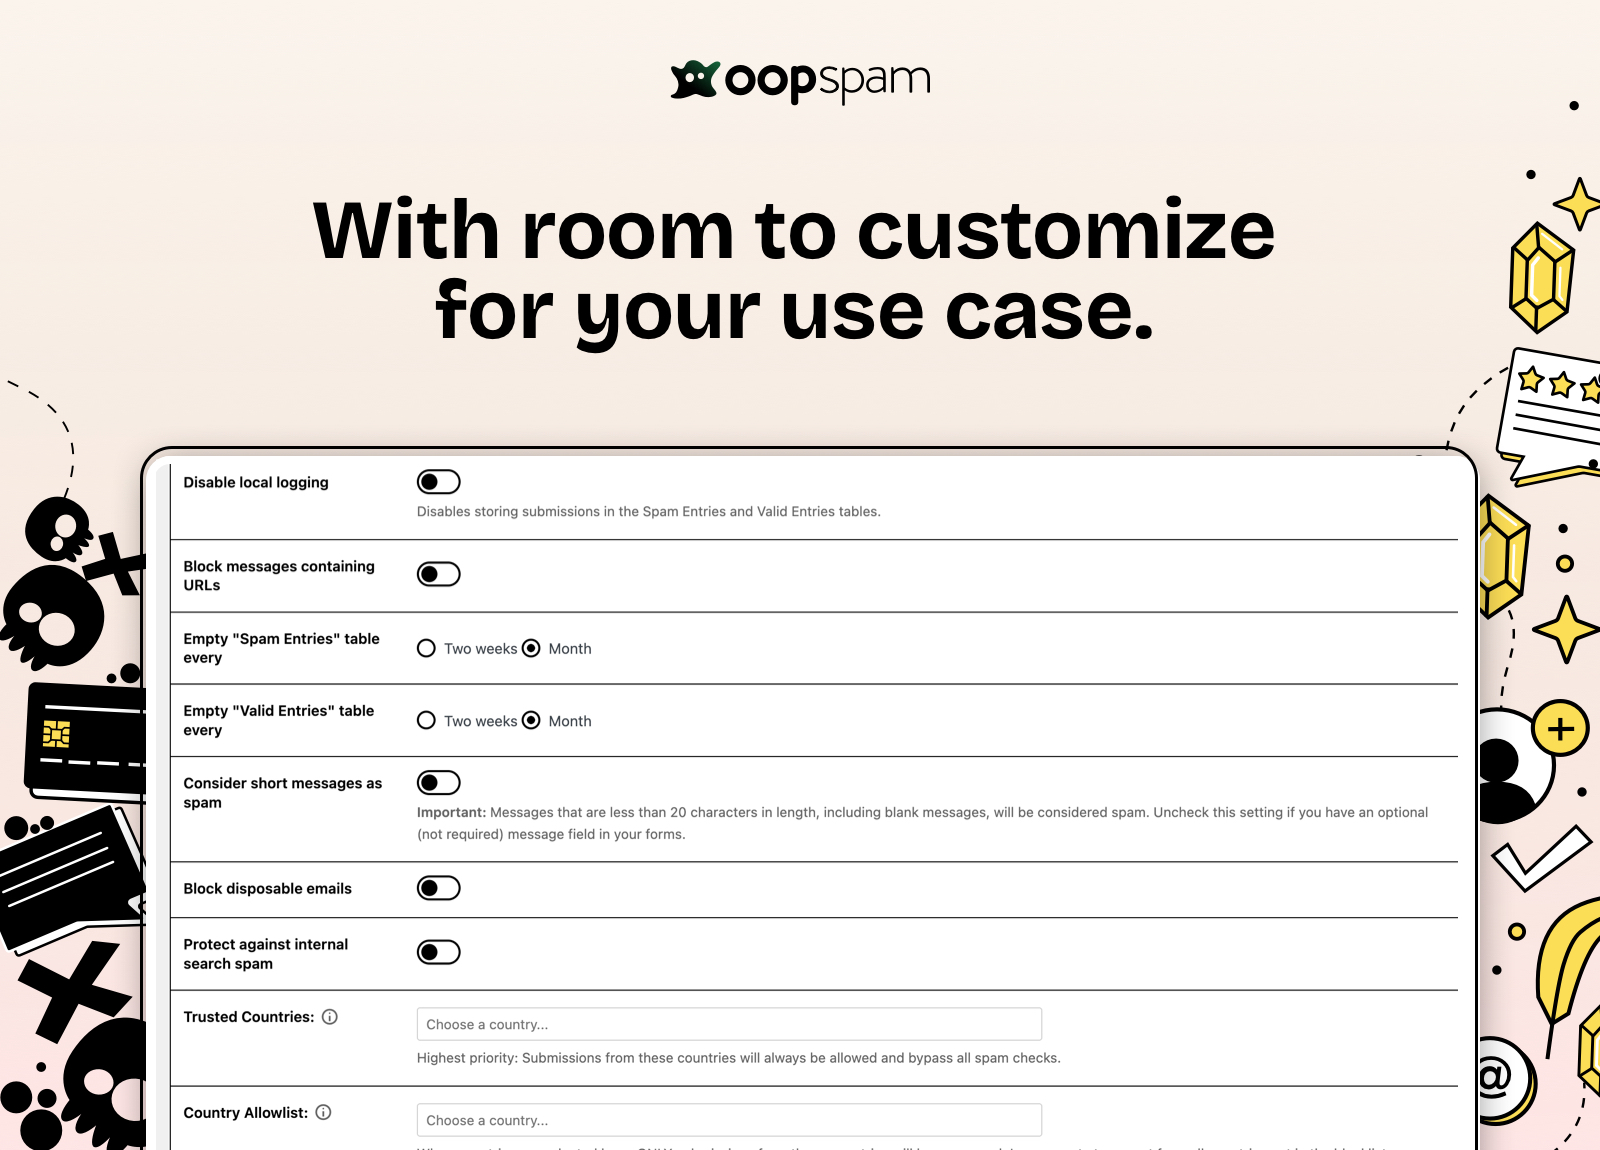
- Filter inzendingen op land en taal, en blokkeer VPN’s en andere bronnen met een hoog risico.
- Gebruik snelheidsbeperking, handmatige besturingselementen, gedetailleerde logs en exports om spam effectief te beheren.
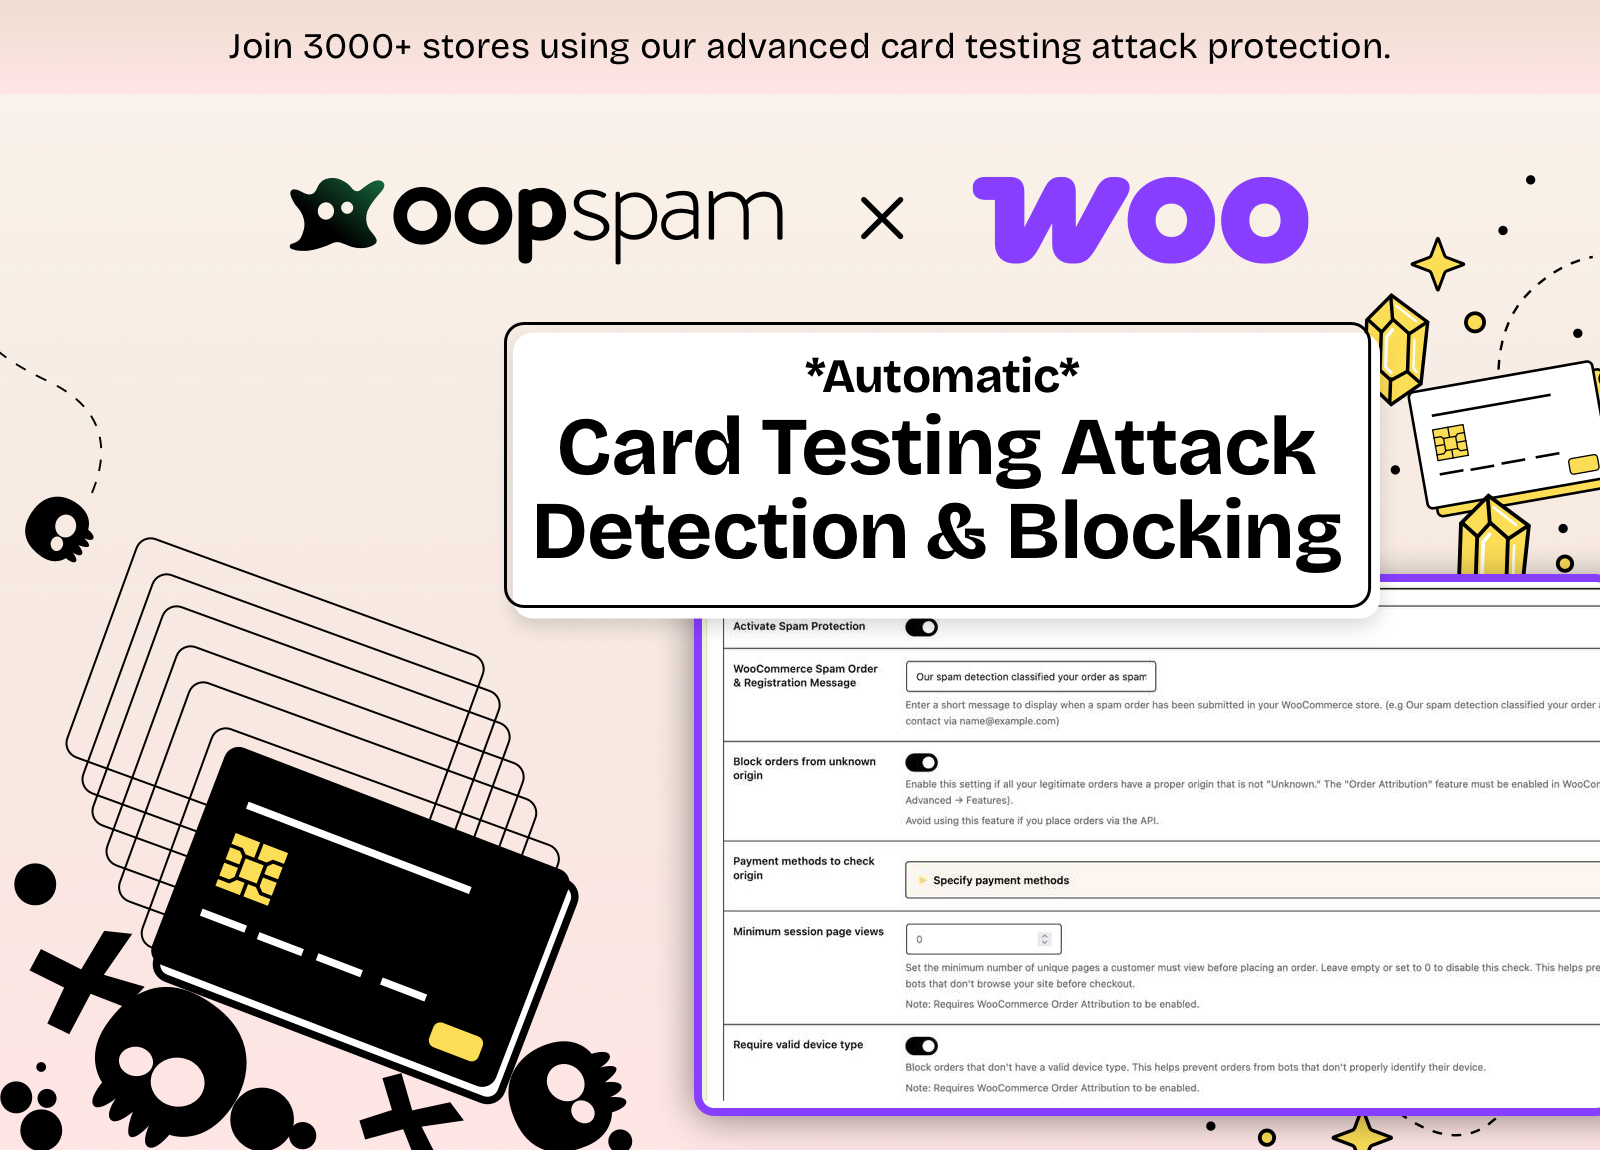
- Bescherm het afrekenen in WooCommerce tegen spam en kaarttesten, en gebruik één API-sleutel voor onbeperkt veel sites.
Wat onze gebruikers zeggen
“Het heeft alle spam verwijderd, en zelfs de noodzaak van CAPTCHA. De setup is snel en de interface is intuïtief.” – @gotmick
“Zeer responsive ondersteuning en een zeer responsief ontwikkelteam. De klantenservice was uitstekend, de reactietijd was direct en problemen werden meteen opgelost.” – @viv18germany
“Pricing is perfect for agencies as they do tiers by actual # of API calls and no limit on the number of sites you can install this on.” – @squarecandy
In cijfers
- Meer dan 3,5 miljoen dagelijks beschermde sites
- 1B+ spampogingen geblokkeerd
- 99,9% detectienauwkeurigheid
- 24/7 klantenondersteuning
- Meer dan 500 miljoen schadelijke IP’s en e-mailadressen in onze database
Ondersteunde formulier- & reactieoplossingen:
- WordPress login, registratie en wachtwoord vergeten
- WooCommerce bestelling & registratie
- BuddyPress
- Elementor Forms
- Elementor Atomic Forms
- Ninja Forms
- Gravity Forms
- Kadence Form Block en Form (Adv) Block
- Fluent Forms
- Breakdance Forms
- WS Form
- WPDiscuz
- Forminator
- WPForms
- Formidable Forms
- Contact Form 7
- Bricks Forms
- Toolset Forms
- Piotnet Forms
- GiveWP Donation Forms
- MailPoet
- Beaver Builder Contact Form
- Ultimate Member
- MemberPress
- Paid Memberships Pro
- Jetpack Forms
- MC4WP: Mailchimp for WordPress
- SureForms
- Super Forms
- SureCart
- FluentCart
- QuForm
- HappyForms Pro
- Avada Forms
- MetForm
- ACF Frontend Forms
- Newsletters by Tribulant
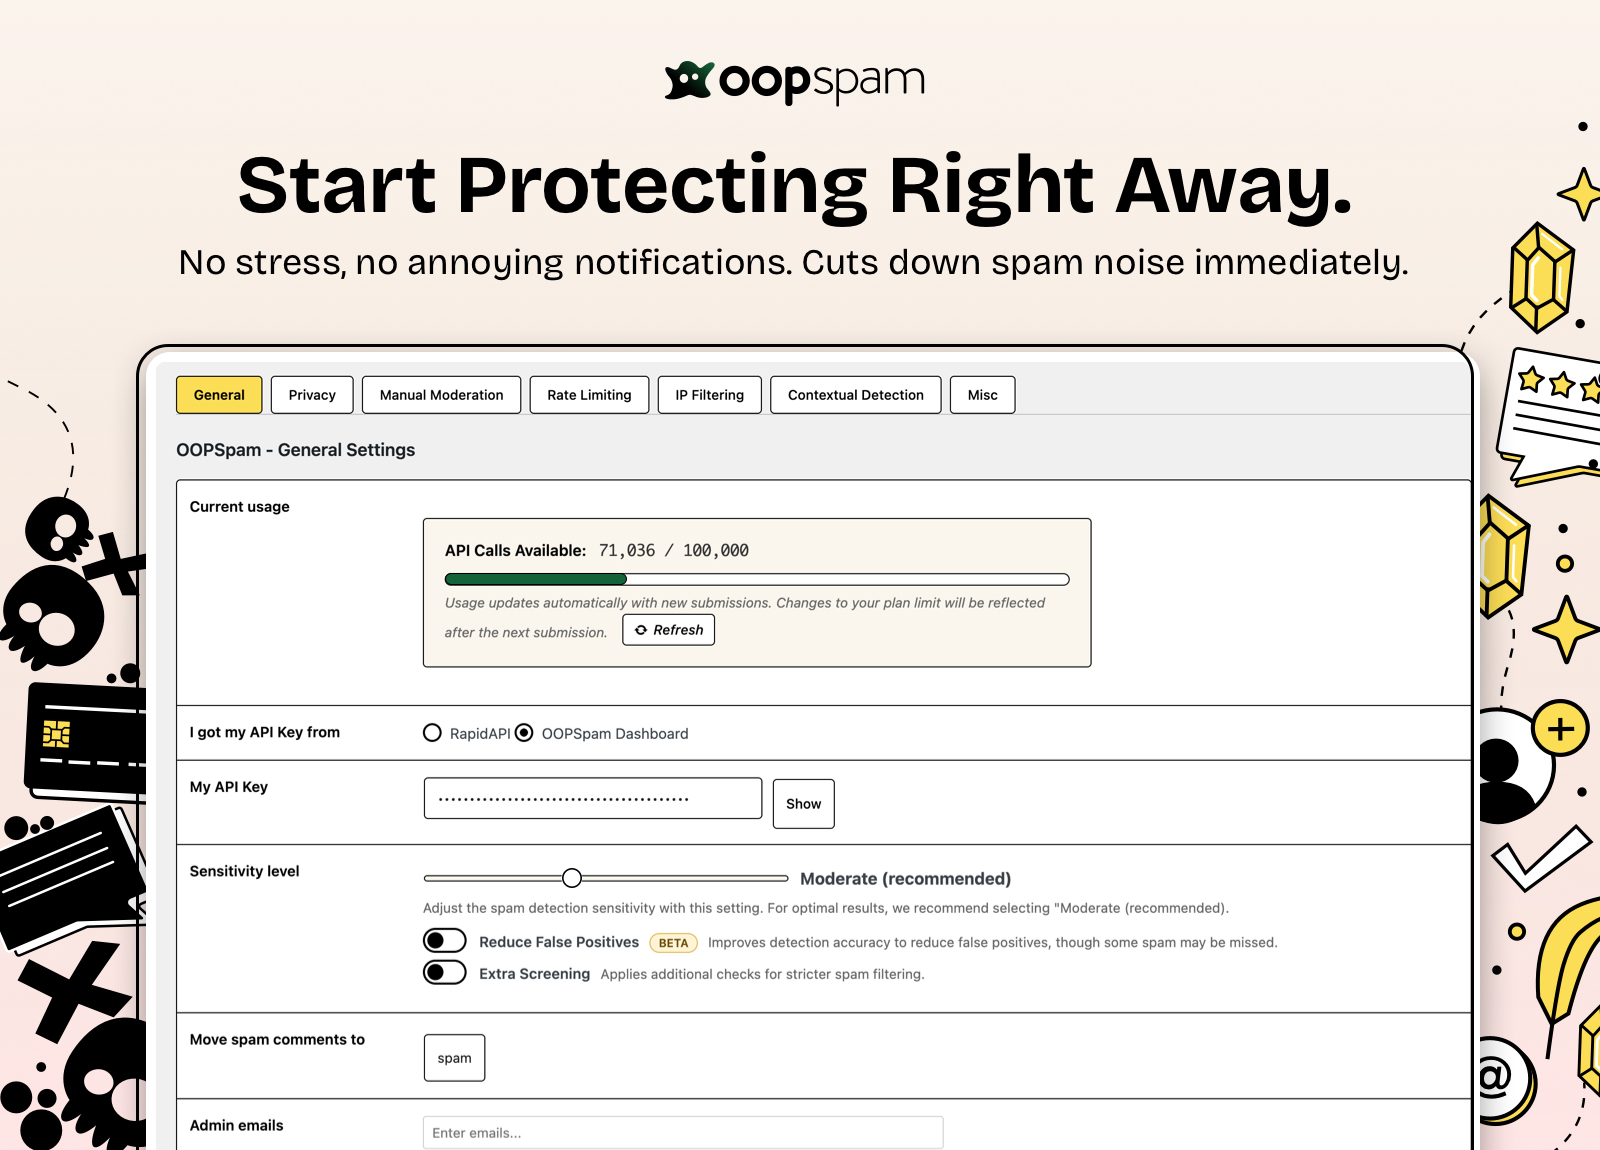
oopspam Anti-Spam WordPress plugin requires minimal configuration. Check out our comprehensive WordPress guide for detailed setup instructions. To get started quickly, get a key and paste it into the appropriate setting field under Settings=>oopspam Anti-Spam. If you have a contact form plugin, make sure you enable spam protection on the settings page.
Please note: This is a premium plugin. You need an oopspam Anti-Spam API key to use the plugin. Each account comes with 40 free spam checks per month.
If you already use oopspam on other platforms, you can use the same API key for this plugin.
Schermafbeeldingen
Installatie
You can install oopspam Anti-Spam plugin both from your WordPress admin dashboard and manually.
INSTALL oopspam Anti-Spam FROM WITHIN WORDPRESS
- Ga naar de pluginpagina in je dashboard en selecteer “Nieuwe toevoegen”;
- Zoek naar “oopspam”;
- Activate oopspam Anti-Spam from your Plugins page;
- Go to oopspam Anti-Spam=>Settings
INSTALL oopspam Anti-Spam MANUALLY
- Upload de map “oopspam-anti-spam” naar de folder /wp-content/plugins/;
- Activate the oopspam Anti-Spam plugin through the ‘Plugins’ menu in WordPress;
- Go to oopspam Anti-Spam=>Settings
NA ACTIVERING
Volg deze korte setupstappen nadat je de plugin hebt geactiveerd:
- Register on the oopspam Dashboard and copy your API key
- Go to oopspam Anti-Spam=>Settings in your WordPress dashboard
- Plak de sleutel in het veld “Mijn API-sleutel”
- Select “oopspam Dashboard” from the “I got my API Key from” setting
- Als je een contactformulier-plugin gebruikt, zorg er dan voor dat de optie “Spambeveiliging activeren” voor die plugin is aangevinkt
Dat is alles! Je formulieren zijn nu beschermd tegen spam. De plugin werkt automatisch op de achtergrond, zonder dat er extra configuratie nodig is.
Voor geavanceerde configuratieopties en gedetailleerde gebruiksinstructies kun je onze WordPress documentatie bekijken.
FAQ
-
While Akismet focuses primarily on comment spam, oopspam offers comprehensive protection for all forms of submissions:
– Protects ALL form types (comments, contact forms, registration, etc.) out of the box
– No need to share user data with third parties
– Includes country blocking and language filtering
– Provides detailed analytics and reporting
– Works silently without impacting user experience
– One API key works across unlimited websites -
How does oopspam compare to CleanTalk?
-
oopspam offers several advantages over CleanTalk:
– Higher accuracy (99.9%) with advanced machine learning
– No JavaScript required, improving site performance
– Better privacy with optional IP/email analysis
– More granular controls for geographic restrictions
– Unlimited websites with one API key
– 24/7 responsive support -
Moet ik een CAPTCHA of andere uitdagingen oplossen?
-
No! oopspam works completely in the background without any user interaction required. This means:
– No puzzles or challenges
– No impact on conversion rates
– Full accessibility compliance
– Better user experience -
Hoeveel API-oproepen heb ik nodig?
-
1 API-oproep = 1 spamcontrole
Wanneer iemand een formulier op je site verzendt, telt dat als één API-oproep. Het gratis abonnement bevat 40 oproepen om de dienst te testen. Hier is een algemene richtlijn:
– Het Freelance-abonnement (100.000 API-oproepen) dekt doorgaans ongeveer 100 sites
– Een gemiddelde site ontvangt dagelijks 20-50 formulierinzendingen
– Om je behoefte in te schatten, tel je je maandelijkse formulierinzendingen over al je sitesNeem contact met ons op als je hulp nodig hebt bij het inschatten van je behoefte.
-
Is oopspam GDPR compliant?
-
Yes! oopspam is fully GDPR compliant:
– No data stored on our servers by default
– Optional IP and email analysis
– All logs stored in your WordPress database
– Ability to remove sensitive information from messages -
Ondersteunt de plugin WP-CLI?
-
Yes. oopspam Anti-Spam ships with a
wp oopspamcommand. You can view the plugin status (wp oopspam status), read and change settings (wp oopspam get/wp oopspam set), and export/import the full configuration (wp oopspam export/wp oopspam import). Runwp help oopspamfor the full reference or check out our WordPress guide.
Beoordelingen


Bijdragers & ontwikkelaars
“oopspam Anti-Spam: Spam Protection for WordPress Forms & Comments (No CAPTCHA)” is open source software. De volgende personen hebben bijgedragen aan deze plugin.
Bijdragers
“oopspam Anti-Spam: Spam Protection for WordPress Forms & Comments (No CAPTCHA)” is vertaald in 1 locale. Dank voor de vertalers voor hun bijdragen.
Interesse in ontwikkeling?
Bekijk de code, haal de SVN repository op, of abonneer je op het ontwikkellog via RSS.
Changelog
1.2.86
- FIX: Fixed a fatal error on servers without the PHP mbstring extension.
- FIX: The spam report email no longer requires the mbstring extension.
1.2.85
- NEW: Added support for FluentCart
1.2.84
- IMPROVEMENT: UI updates.
1.2.83
- OPGELOST: CSS problemen met de slider van de instelling “Gevoeligheidsniveau” zijn opgelost.
- IMPROVEMENT: Added the plugin text domain and marked previously untranslatable strings.
- IMPROVEMENT: Increased the minimum required WordPress version to 4.6.
1.2.82
- FIX: Resolved an error in the MC4WP integration.
1.2.81
- NEW: Blocked keywords now comes pre-filled with spam words in English, Russian, and Chinese.
- IMPROVEMENT: Minor UI and UX improvements
1.2.80
- NEW: Added support for Super Forms
- IMPROVEMENT: Preserve and display current settings in the Setup Wizard
1.2.79
- NEW: Added support for the Abilities API.
- NEW: Added the plugin to Settings Connectors for convenient API key management.
1.2.78
- FIX: Tools import/export page is now a standalone submenu page with its styles loaded correctly
1.2.77
- NEW: WP-CLI support:
wp oopspamcommands to view, change, export, and import settings - NEW: Import/Export settings from the plugin interface (Tools submenu)
- NEW: Bulk-apply settings across all sites with
--all-siteson multisite networks - IMPROVEMENT: Exposed
Block Cloud ProvidersandExtra Screeningsettings in the Setup Wizard
1.2.76
- NEW: [WooCommerce] Block orders in bulk or individually under WooCommerce Orders
- IMPROVEMENT: Prevent email notifications in Kadence Forms
- FIX: Handle blank dates in Valid and Spam Entries tables
1.2.75
- IMPROVEMENT: Improved meta-logs collection in the WooCommerce integration.
- IMPROVEMENT: Admin notice dismissals are now remembered.
1.2.74
- NEW: Form ID in the Form and Valid Entries tables now displays the form title/name on hover.
- VERBETERING: snelheidsbeperking controleert nu lopende aanvragen om racecondities te helpen voorkomen.
- FIX: The timezone setting now uses UTC when displaying dates in the Form and Valid Entries tables.
- FIX: The date range filter in the Form and Valid Entries tables now respects the database timezone.
1.2.73
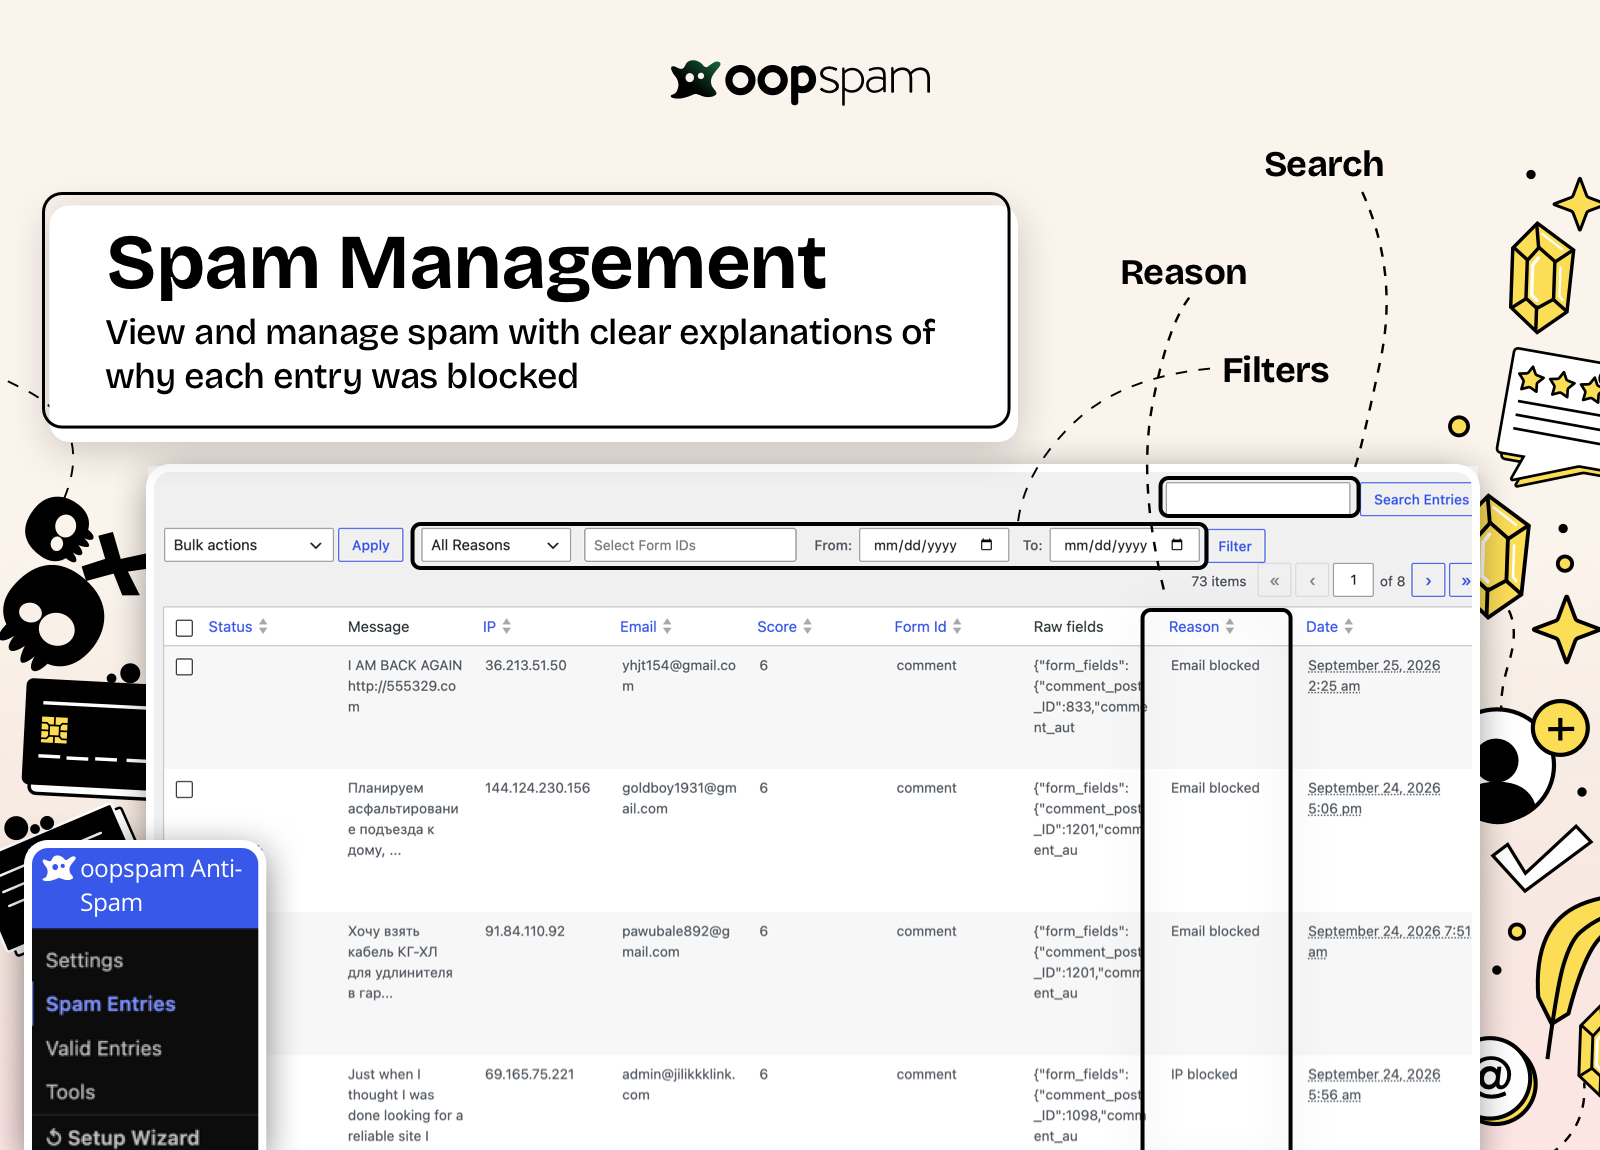
- NEW: Added a new date range filter to the Form and Spam Entries tables
- FIX: Fixed a double time zone conversion for the time zone setting.
1.2.72
- NEW: Added “Undo” action to reverse spam and non-spam reported submissions
- IMPROVEMENT: Pagination is preserved when reporting entries in Valid and Spam Entries tables
- FIX: Added additional privilege validation checks for user actions
1.2.71
- NEW: Added “Entries table timezone” setting to customize timezone display for logs, and spam reports.
- IMPROVEMENT: Small UI improvements
1.2.70
- NEW: Added support for Elementor Atomic Forms
1.2.69
- NEW: Added an experimental “Smart Accuracy” feature with additional checks to help reduce false positives.
- NEW: Added an experimental “Extra Screening” feature with additional checks for stricter spam filtering.
- IMPROVEMENT: Manual Moderation -> Blocked Emails and Allowed Emails now support the @.com pattern.
1.2.68
- IMPROVEMENT: Added spam protection to the WordPress login and lost password forms.
- IMPROVEMENT: Minor UI improvements.
1.2.67
- NEW: Added oopspam_check_spam function to check custom forms for spam.
- IMPROVEMENT: Send the “Spam Summary Report” to multiple recipients.
1.2.66
- NEW: Added “Spam Summary Report” feature for scheduled email reports
1.2.65
- NEW: Added support for Newsletters by Tribulant PRO version
- FIX: URLs are not being captured in comment content.
1.2.64
- NEW: Added support for Newsletters by Tribulant
- IMPROVEMENT: [Breakdance] Added an option to enable or disable spam protection.
1.2.63
- NEW: [WooCommerce] Added “Max failed payment attempts per IP” velocity protection setting.
- NEW: [WooCommerce] Added “Failed payment time window (hours)” setting for velocity checks.
- NEW: [WooCommerce] Added “Block repeated same-amount orders” and “Same-amount order window (hours)” settings.
- IMPROVEMENT: [WooCommerce] Improved Classic and Block Checkout field handling via
WC_Order. - FIX: [WooCommerce] Fixed Block Checkout validation flow for
WC_Orderhandling. - OPGELOST (BEVEILIGING): [Contact Form 7] Opgeslagen XSS in de spam-/geldige vermeldingen van wp-admin is voorkomen.
- FIX: [Settings UI] Fixed tooltip visibility in WordPress admin.
1.2.62
- NEW: [WooCommerce] Added “Block orders with specific billing addresses” setting to block orders matching known fraudulent addresses
- FIX: [WooCommerce] Fixed JSON parse error (“SyntaxError: Unexpected token”) on block-based checkout when an order is blocked
1.2.61
- IMPROVEMENT: Better contextual spam detection guide
- IMPROVEMENT: New, clearer settings page design
- IMPROVEMENT: Simplified setting names for easier understanding
1.2.60
- NEW: Added notice to encourage users behind proxies (e.g., Cloudflare) to enable “Trust proxy headers” for accurate IP detection
- IMPROVEMENT: Better metadata in local logging for easier debugging
- IMPROVEMENT: Display clear reason for the API error
1.2.59
- IMPROVEMENT: Wrapped all debug error_log() calls in WP_DEBUG checks for better production performance
- IMPROVEMENT: Replaced wp_redirect() with wp_safe_redirect() for better security compliance
- FIX: Addressed “too many requests” errors when the API key is not provided
1.2.58
- NEW: [WooCommerce] Order origin checks now respect Manual Moderation -> Allowed IPs settings
- IMPROVEMENT: [WooCommerce] “Block orders with specific total amounts” setting now accepts multiple amounts (one per line)
- FIX: [WooCommerce] Prevented duplicate spam entries when blocking orders with specific total amounts
1.2.57
- FIX: Prevented rate limiting notices from appearing after upgrade
1.2.56
- IMPROVEMENT: Added missing countries to Blocked and Allowed Countries lists
- IMPROVEMENT: Manual Moderation settings now take precedence over rate limiting
- FIX: General code quality improvements and bug fixes
1.2.55
- FIX: Fixed “Do not analyze IP addresses” and “Do not analyze Email addresses” settings not working
- FIX: [Ninja Forms] Fixed spam error message not displaying
1.2.54
- NIEUW: Ondersteuning voor ACF Frontend Forms toegevoegd
- NEW: Added “Email admin when marked as not spam” setting
- NEW: Added “Trust proxy headers” setting (required for proper IP detection behind proxies)
- FIX: Enhanced security to prevent IP spoofing attacks – requires new “Trust proxy headers” setting
- FIX: All the rate limiting features now require “Enable rate limiting” to be enabled
1.2.53
- NEW: Added support for MetForm
- IMPROVEMENT: [Forminator] Stop other actions from running when a spam detected
1.2.52
- NEW: Added support for Avada Forms
- IMPROVEMENT: Added missing Caribbean countries to the country lists.
- IMPROVEMENT: UX improvements to the Setup Wizard.
1.2.51
- NEW: [WooCommerce] Added “Block orders with specific total amount” setting to prevent card testing on older WooCommerce versions
- FIX: [WooCommerce] Stop payment processing immediately when validation fails
1.2.50
- NEW: Added “Refresh” button to manually update API usage statistics
- NEW: Added support for BuddyPress registration forms
- IMPROVEMENT: [WooCommerce] Enhanced order attribution validation to prevent bypass attempts in Classic Checkout
1.2.49
- FIX: Fixed issue where setup wizard would appear even when API key was already configured
1.2.48
- NEW: Added interactive setup wizard for easier configuration
- NEW: [WooCommerce] Added “Disable WooCommerce checkout via REST API” setting to prevent API-based attacks
- NEW: [WooCommerce] Added “Minimum session page views” setting to enhance protection against card testing
- NIEUW: [WooCommerce] instelling “Vereis geldig apparaattype” toegevoegd om de bescherming tegen het testen van kaarten te verbeteren
- IMPROVEMENT: Added support for IP ranges in “Manual Moderation -> Blocked IPs” setting (e.g., 192.168.1.0/24)
- IMPROVEMENT: Renamed “Form Ham Entries” to “Valid Entries” for better clarity
- IMPROVEMENT: Verified compatibility with PHP 8.4 and fixed API usage update issues
- IMPROVEMENT: [WooCommerce] Enhanced Order Attribution checks for more accurate spam detection
- FIX: Spam checks now skip customers with previously completed orders to prevent false positives
- FIX: Resolved issue where empty “Trusted Countries” setting incorrectly allowed submissions
1.2.47
- NEW: Added a new setting: “Trusted Countries (always bypasses spam checks)”
- IMPROVEMENT: WooCommerce orders now use our IP detection method to capture the real IP instead of proxy IPs
- IMPROVEMENT: UX improvements for geo-location settings
1.2.46
- IMPROVEMENT: Enhanced IP address detection for Elementor Forms integration
- FIX: Fixed custom spam messages not falling back to default when empty across all form integrations
1.2.45
- NEW: Added support for HappyForms
- IMPROVEMENT: Enhanced logging of block reasons in the comment system
1.2.44
- NEW: Added support for QuForm
- FIX: Prevent the pre-comment approval hook from executing multiple times
1.2.43
- FIX: [WooCommerce] Fixed undefined function error in scheduled payments by enforcing global namespace.
1.2.42
- FIX: [WooCommerce] Prevent Moneris payment details from being stored in raw logs.
1.2.41
- NIEUW: compatibiliteit met de Gravity Forms Partial Entries Add-On toegevoegd.
1.2.40
- FIX: “The main content field ID (optional)” setting was not capturing multiple field data in Contact Form 7.
1.2.39
- NEW: Added support for SureCart
1.2.38
- IMPROVEMENT: Enhanced IP detection in the WordPress comment system to account for proxy usage
1.2.37
- IMPROVEMENT: Enhanced method for capturing user’s IP address
1.2.36
- NEW: Introduced “Contextual Spam Detection” to analyze spam based on content and website context.
- IMPROVEMENT: Refined API usage metrics for tracking.
1.2.35
- NIEUW: De mogelijkheid geïntroduceerd om spamvermeldingen op formulier-ID te filteren.
- IMPROVEMENT: Enhanced the user experience for displaying
Current usage. - FIX: Addressed issues with the
DeleteandEmail adminactions in the Spam Entries table.
1.2.34
- FIX: Ensure sessions are initiated and terminated correctly only when the ‘Minimum Time Between Page Load and Submission (in seconds)’ setting is active.
1.2.33
- NEW: Introduced a new setting: ‘Rate Limiting -> Minimum Time Between Page Load and Submission’
- IMPROVEMENT: Excluded rate limiting from internal search spam protection
- IMPROVEMENT: [Breakdance] Disabled email notifications for detected spam submissions
1.2.31
- NEW: [WooCommerce] Added “Payment methods to check origin” setting to restrict origin checks to selected payment methods.
- NEW: Automatically report comments as spam or ham to oopspam when flagged within the WordPress comment system.
- NEW: Introduced “Disable local logging” setting to disable logging in the Form Spam and Valid Entries tables.
- NEW: Added global settings for “Log submissions to oopspam” and “Disable local logging” using constants:
define('OOPSPAM_DISABLE_LOCAL_LOGGING', true);define('OOPSPAM_ENABLE_REMOTE_LOGGING', true);
- IMPROVEMENT: Enhanced Spam Entries table to display submissions not analyzed due to rate limiting or API errors.
- VERBETERING: het bericht met het verzoek om een beoordeling is verwijderd voor een schonere gebruikerservaring. (Maar overweeg gerust om een beoordeling achter te laten <3)
- IMPROVEMENT: [SureForms] Added support for custom messages.
- IMPROVEMENT: [Gravity Forms] Replaced anonymous functions with named functions for better integration support.
1.2.29
- NEW: Added support for Multi-site/Network installations
- NIEUW: De mogelijkheid toegevoegd om spamvermeldingen op detectiereden te filteren
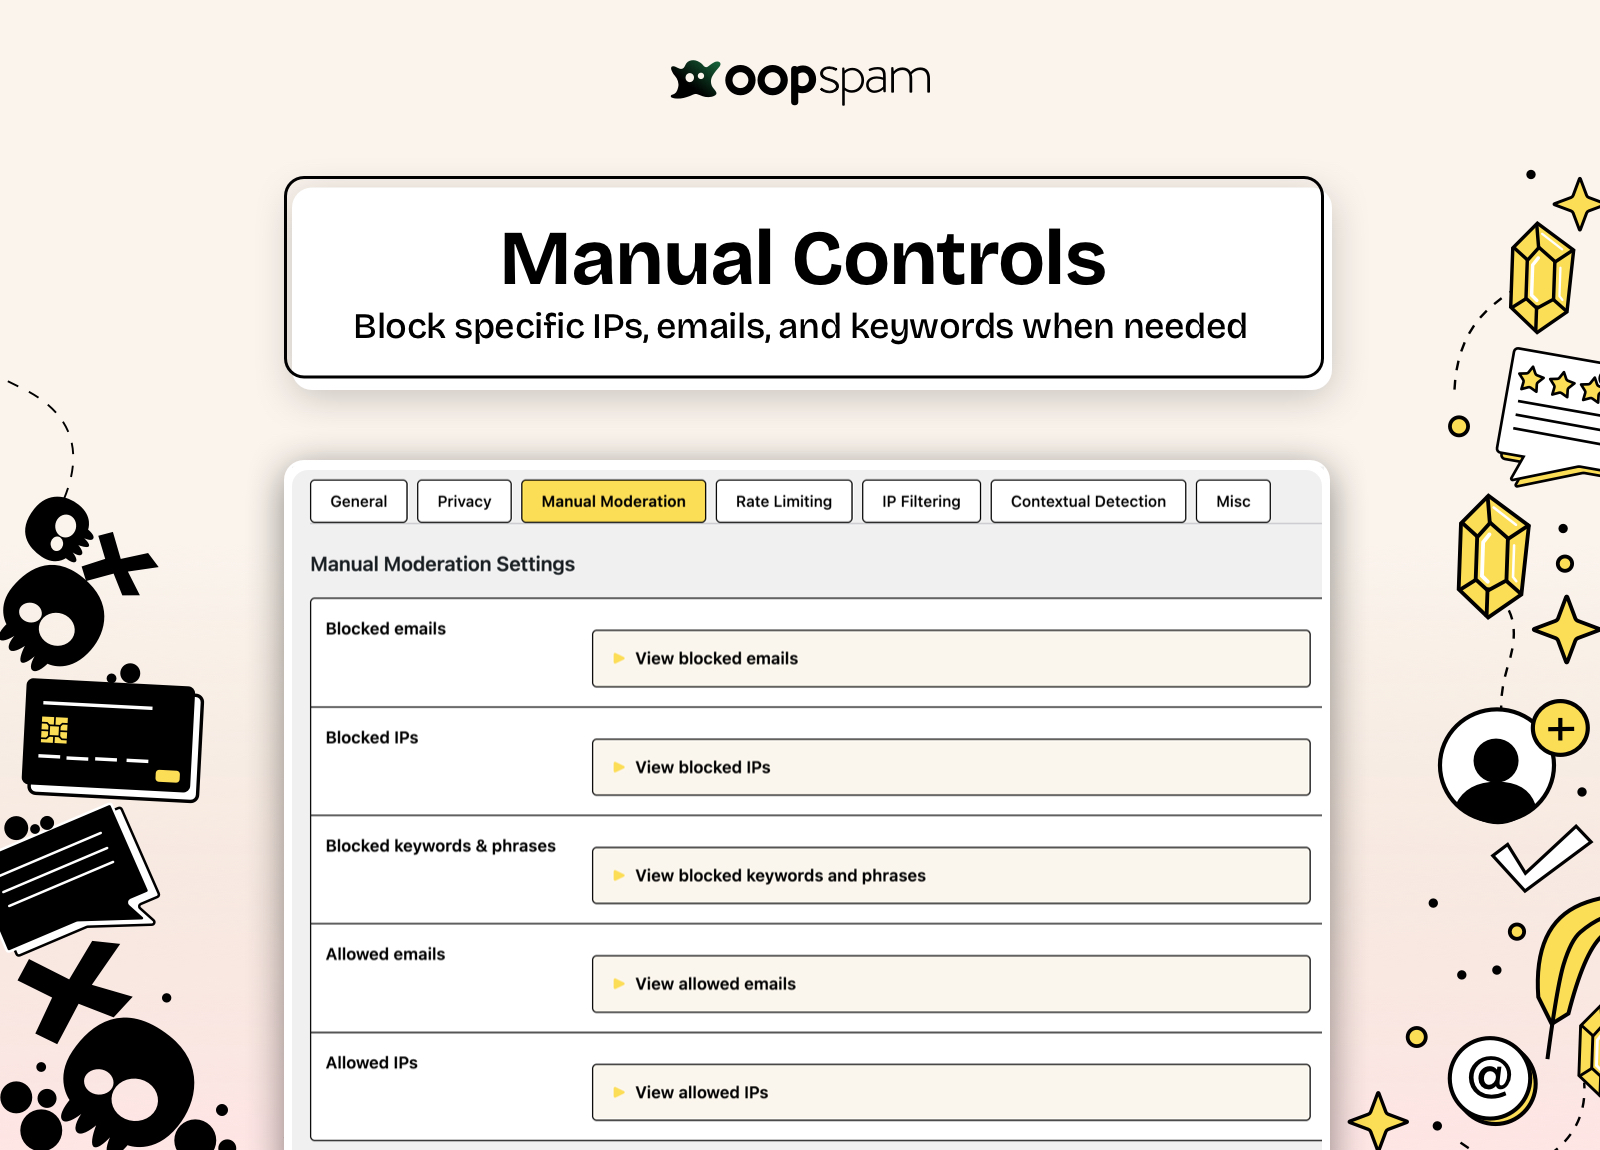
- IMPROVEMENT: Manually blocked IPs and emails now take precedence over manually allowed ones
- FIX: Prevented storing password field values in logs during WooCommerce registration
1.2.28
- NEW: Added IP Filtering options to block VPNs and Cloud Providers
- NEW: Ability to define the global API key in wp-config.php using
define( 'OOPSPAM_API_KEY', 'YOUR_KEY' ) - IMPROVEMENT: Added quick links to “Add countries in Africa” & “Add countries in the EU” in the country blocking settings
- IMPROVEMENT: Enhanced IP detection for WordPress comments
- FIX: Resolved issue with textarea field detection in Fluent Forms
- FIX: Fixed array validation issue
1.2.27
- NEW: Added North Korea to the list of supported countries
- IMPROVEMENT: [WooCommerce] Enhanced blocking of orders from unknown origins for both the Legacy API and the classic checkout
- IMPROVEMENT: [Kadence] Prevented email notifications in the Kadence Advanced Form Block
- FIX: Resolved error occurring during rate limiting deactivation
1.2.26
- NEW: Added integration support for SureForms plugin
- NEW: [WooCommerce] Added option to toggle honeypot field protection
- IMPROVEMENT: [Fluent Forms] Implemented more reliable IP address detection
- FIX: Added fallback handling for missing API request headers
1.2.25
- IMPROVEMENT: [Gravity Forms] Enhanced method for capturing user’s IP address
- FIX: Resolved conflict with Breakdance
1.2.24
- IMPROVEMENT: Enhanced method to prevent naming collisions with other plugins
- IMPROVEMENT: [Jetpack Forms] Spam submissions are now categorized under Feedback->Spam
- IMPROVEMENT: [Jetpack Forms] Improved handling of
textareafields - FIX: [Gravity Forms] Privacy settings were not being respected
1.2.23
- NEW: Added a new rate-limiting setting: “Restrict submissions per Google Ads lead”
1.2.22
- NEW: Added support for MC4WP: Mailchimp for WordPress
- FIX: Added prefixes to functions to prevent conflicts with other plugins
1.2.21
- IMPROVEMENT: [WooCommerce] Exclude honeypot field detection when allowed in Manual Moderation settings.
- IMPROVEMENT: [WooCommerce] Enhanced honeypot field functionality for better accuracy.
- IMPROVEMENT: Form Spam and Ham Entries tables now display the country name associated with an IP address.
- IMPROVEMENT: Minor UX enhancements for Allowed and Blocked Country settings.
1.2.20
- NEW: Added support for Jetpack Form
- IMPROVEMENT: Form Spam and Ham Entries tables now delete entries older than the selected interval instead of completely clearing the entire table
1.2.19
- IMPROVEMENT: Extended WS Form support to include the Lite version
- FIX: Removed an unnecessary query during the rate limit table creation
1.2.18
- NEW: [WooCommerce] “Block orders from unknown origin” setting for the Block Checkout
1.2.17
- NEW: Added bulk reporting functionality for both Spam Entries and Valid Entries tables
- IMPROVEMENT: [WooCommerce] Enhanced detection of spam targeting the WooCommerce Block Checkout
- IMPROVEMENT: Resolved layout shifts caused by notices from other plugins
- IMPROVEMENT: [WooCommerce] Removed first name validation to prevent false positives
1.2.16
- NEW: Rate limiting for submissions per IP and email per hour
- NEW: [Forminator] Specify content field by Form ID and Field ID pair
- NEW: [Forminator] Combine multiple field values for the
The main content fieldsetting - IMPROVEMENT: [GiveWP] Reject donations with invalid payment gateways
- IMPROVEMENT: Enhanced honeypot implementation in WooCommerce
- IMPROVEMENT: Use WooCommerce’s internal function for IP detection
- VERBETERING: Verbeterde opmaak en meer gegevens in e-mailmeldingen naar de beheerder
- IMPROVEMENT: Added Sucuri proxy header support in IP detection
1.2.15
- NIEUW: Ondersteuning voor het Kadence Form (Advanced) Block toegevoegd
- NEW: Automatically send flagged spam comments to oopspam for reporting
1.2.14
- NEW: Added
oopspam_woo_disable_honeypothook to disable honeypot in WooCommerce - IMPROVEMENT: Reorganized privacy settings under the Privacy tab for better clarity
- IMPROVEMENT: General UX enhancements for a smoother experience
- FIX: Resolved issue where WooCommerce blockings were not logged
1.2.13
- NEW: View spam detection reasons in the Spam Entries table
- NEW: Report entries flagged as spam in Gravity Forms to oopspam
- NEW: Report entries flagged as not spam in Gravity Forms to oopspam
- IMPROVEMENT: Admin comments bypass spam checks
1.2.12
- NEW:
Block messages containing URLssetting
1.2.11
- NEW: Paid Memberships Pro support
1.2.10
- FIX: Broken
The main content field ID (optional)setting
1.2.9
- NEW: MemberPress integration
- IMPROVEMENT: Detect Cloudflare proxy in IP detection
1.2.8
- NEW: Integrated spam submission routing to Gravity Forms’ Spam folder
- NEW: Introduced Allowed IPs and Emails settings in Manual Moderation
- NEW: Implemented automatic allowlisting of email and IP when an entry is marked as ham (not spam)
- IMPROVEMENT: Enhanced GiveWP integration to capture donor email addresses
- IMPROVEMENT: Optimized content analysis in GiveWP by combining comment, first name, and last name fields
- FIX: Prevent duplicate entries in Blocked Emails and IPs settings
1.2.7
- NEW: Automatic local blocking of email and IP when an item is reported as spam
- IMPROVEMENT: Truncate long messages in Valid Entries and Spam Entries tables
- IMPROVEMENT: Clean up manual moderation data from the database when plugin is uninstalled
- FIX: Correct usage of elements in the settings fields for improved accessibility
- FIX: Resolve dynamic property deprecation warnings
1.2.6
- NEW: [Fluent Forms] Specify content field by Form ID and Field Name pair
- NEW: [Fluent Forms] Combine multiple field values for the ‘The main content field’ setting
- FIX: [Fluent Forms] Fix error when there is no textarea in a form
1.2.5
- NEW: [WS Form] Specify content field by Form ID and Field ID pair
- NEW: [WS Form] Combine multiple field values for the ‘The main content field’ setting
- FIX: Error when “Not Spam” is used in the Spam Entries table
1.2.4
- NEW: “Block disposable emails” setting
- FIX: Broken “Move spam comments to” setting
1.2.3
- NEW: Basic HTML support for error messages in all integrations
- NIEUW: mogelijkheid om meerdere ontvangers in te stellen voor
e-mail naar beheerderin de tabel met spamvermeldingen - NEW: [Gravity Forms] Specify content field by Form ID and Field ID pair
- NEW: [Gravity Forms] Combine multiple field values for the
The main content fieldsetting - IMPROVEMENT: Improved security and accessibility by migrating to a modern UI control library
1.2.2
- NIEUW: [Gravity Forms] Betere compatibiliteit met Gravity Perks Limit Submissions
- IMPROVEMENT: [Gravity Forms] Display error message at top of form instead of next to field
1.2.1
- NEW: [Elementor Forms] Specify content field by Form ID and Field ID pair
- NEW: [Elementor Forms] Combine multiple field values for the
The main content fieldsetting - NEW: Wildcard support for manual email blocking (e.g. *@example.com)
1.2
- NEW: [WPForms] Specify content field by Form ID and Field ID pair
- NEW: [WPForms] Combine multiple field values for the
The main content fieldsetting - FIX: Prevent email notifications for spam comments
- FIX: Send email from site admin instead of form submitter in
E-mail adminsetting
1.1.64/65
- IMPROVEMENT: [WPForms] Use Field Name/Label in
The main content field ID (optional)setting
1.1.63
- NEW: Display a custom error message in Contact Form 7
1.1.62
- NIEUW: Instelling
Deze formulieren niet beschermen. Mogelijkheid om een formulier uit te sluiten van spambeveiliging - NIEUW:
CSV exporterenin de tabellen met spamvermeldingen & geldige vermeldingen - IMPROVEMENT: More reliable IP detection
- IMPROVEMENT: Confirmation prompt before emptying Ham and Spam Entries table
- IMPROVEMENT: Improved styling of the settings page
- IMPROVEMENT: Hide
Blocked countrieswhenDo not analyze IP addressesis enabled
1.1.61
- NEW:
Manual moderationsetting to manually block email, IP and exact keyword. - NEW:
Email adminsetting underSpam Entriesto send submission data to the website admin - FIX: Load plugin Javascript and CSS files only in the plugin settings
1.1.60
- IMPROVEMENT: WS Form integration uses new pre-submission hook. No need to add an action anymore
- NEW: WS Form Spam Message error field
- NEW: Ultimate Member support
1.1.59
- FIX: Error when reporting false positives/negatives
1.1.58
- NEW:
Log submissions to oopspamsetting. Allows you to view logs in the oopspam Dashboard
1.1.57
- FIX: WooCommerce spam filtering applied even when spam protection was off
1.1.56
- NEW:
The main content field IDsetting now supports multiple ids (separated by commas) - NEW: Beaver Builder contact form support
1.1.55
- IMPROVEMENT: A better way to prevent empty messages from passing through
1.1.54
- NEW: Trackback and Pingback protection
- NEW: WP comment logs are available under the Form Spam/Ham Entries tables.
1.1.53
- OPGELOST: WP_Query-waarschuwing in de zoekbeveiliging
1.1.52
- MISC: Compatibility tested with WP 6.4
1.1.51
- VERBETERING: de Bricks Form integratie vereist niet langer dat je een aangepaste actie toevoegt.
1.1.50
- NEW: Breakdance Forms support
- FIX: Failed nonce verification in cron jobs that empty spam/ham entries