Beschrijving
Uitgebreide WordPress login beveiligingsplugin
Melapress Login Security stelt je in staat om moeiteloos login beveiligingsbeleid in te stellen die je stevig in de bestuurdersstoel van je WordPress sites plaatst. Beleid is zeer aanpasbaar en gedetailleerd en kan worden geïmplementeerd per gebruikersrol of site-breed voor volledige controle over de beveiliging van je WordPress login processen.
Gebruik de gratis editie van Melapress Login Security om WordPress wachtwoordvereisten te implementeren, zoals minimale lengte en complexiteitsregels. De plugin stelt je ook in staat om wachtwoordverloopbeleid in te stellen, wachtwoordhergebruik te voorkomen, mislukte inlogpogingen te beperken en automatisch inactieve gebruikersaccounts uit te schakelen, naast andere dingen. Dit helpt je:
- Voorkom ongeautoriseerde login pogingen
- Bescherm tegen brute force aanvallen
- Voldoe aan de AVG/GDPR met een login toestemmingsbericht
🔐 Functies lijst
Een veilige WordPress login begint hier. Ontdek alle functies die zijn inbegrepen bij de gratis editie van Melapress Login Security:
Stel wachtwoordbeleid in
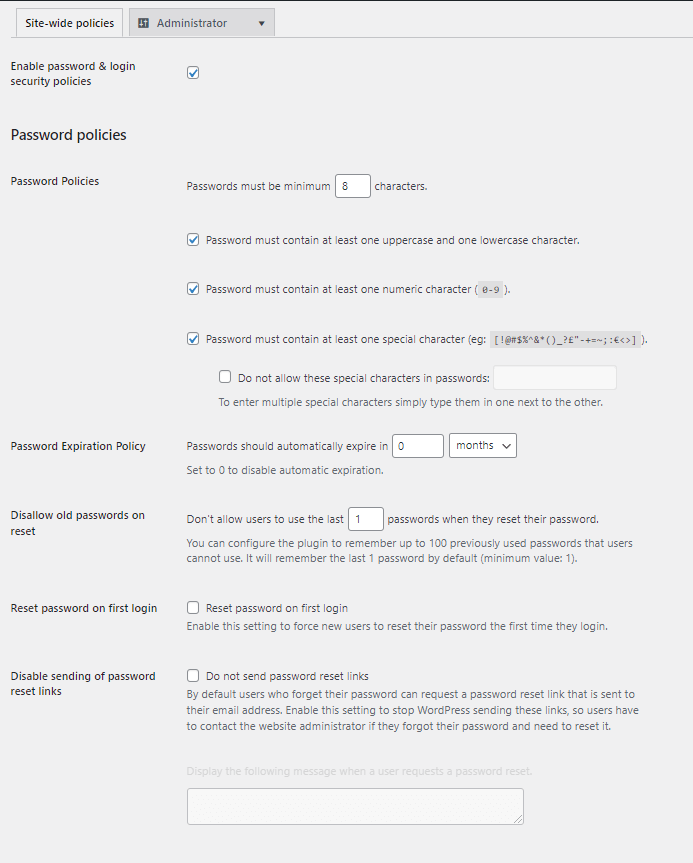
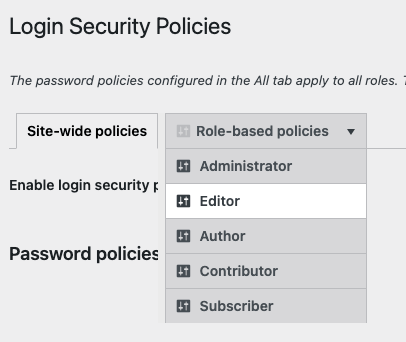
Sterke wachtwoorden zijn je eerste verdedigingslinie tegen kwaadwillenden die toegang willen krijgen tot je site. Stel wachtwoordvereisten in om ervoor te zorgen dat gebruikers sterke wachtwoorden instellen. Stel beleid in per gebruikersrol of site-breed en definieer beleidsprioriteit voor gebruikers met meerdere rollen.
- Stel minimum wachtwoordlengte in
- Require uppercase and lowercase characters, numbers, and special characters
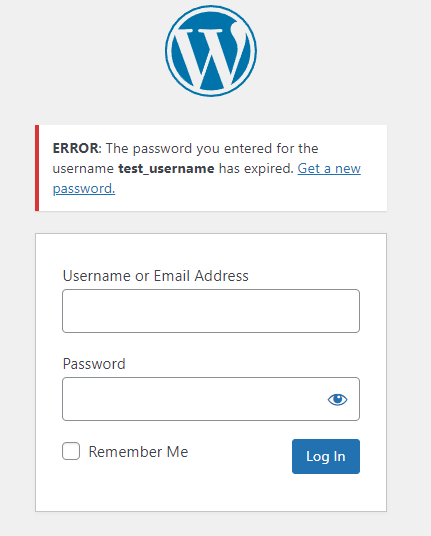
- Stel een automatisch wachtwoordverloop beleid in en adviseer gebruikers wanneer hun wachtwoord bijna verloopt
- Voorkom dat gebruikers wachtwoorden opnieuw gebruiken
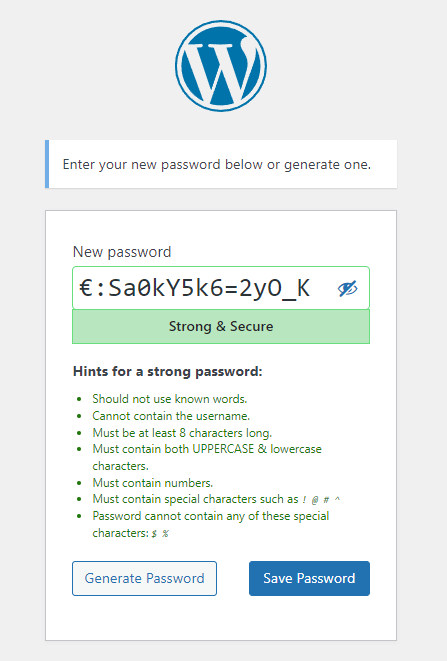
- Geef gebruikers nuttige instructies tijdens de wachtwoordconfiguratie
- Wachtwoord reset links uitschakelen
- Dwing WordPress wachtwoord reset af bij de eerste login
Beperk login pogingen
Beperk mislukte login pogingen en maak een einde aan brute force aanvallen. Bescherm je login formulier door gebruikersaccounts automatisch uit te schakelen na een aantal mislukte login pogingen. Kies tussen handmatige ontgrendeling door een beheerder of automatische ontgrendeling na een afkoelperiode.
Temporary login without password
Provide temporary and secure login access to third parties, like developers, editors, employees or others, without a password. It works by providing the user with a temporary login link that expires after a certain amount of time, or after a number of uses. This prevents you from having to create new user accounts manually, while simultaneously reducing the security risks associated with old, unused user accounts.
Wijzig WordPress login URL
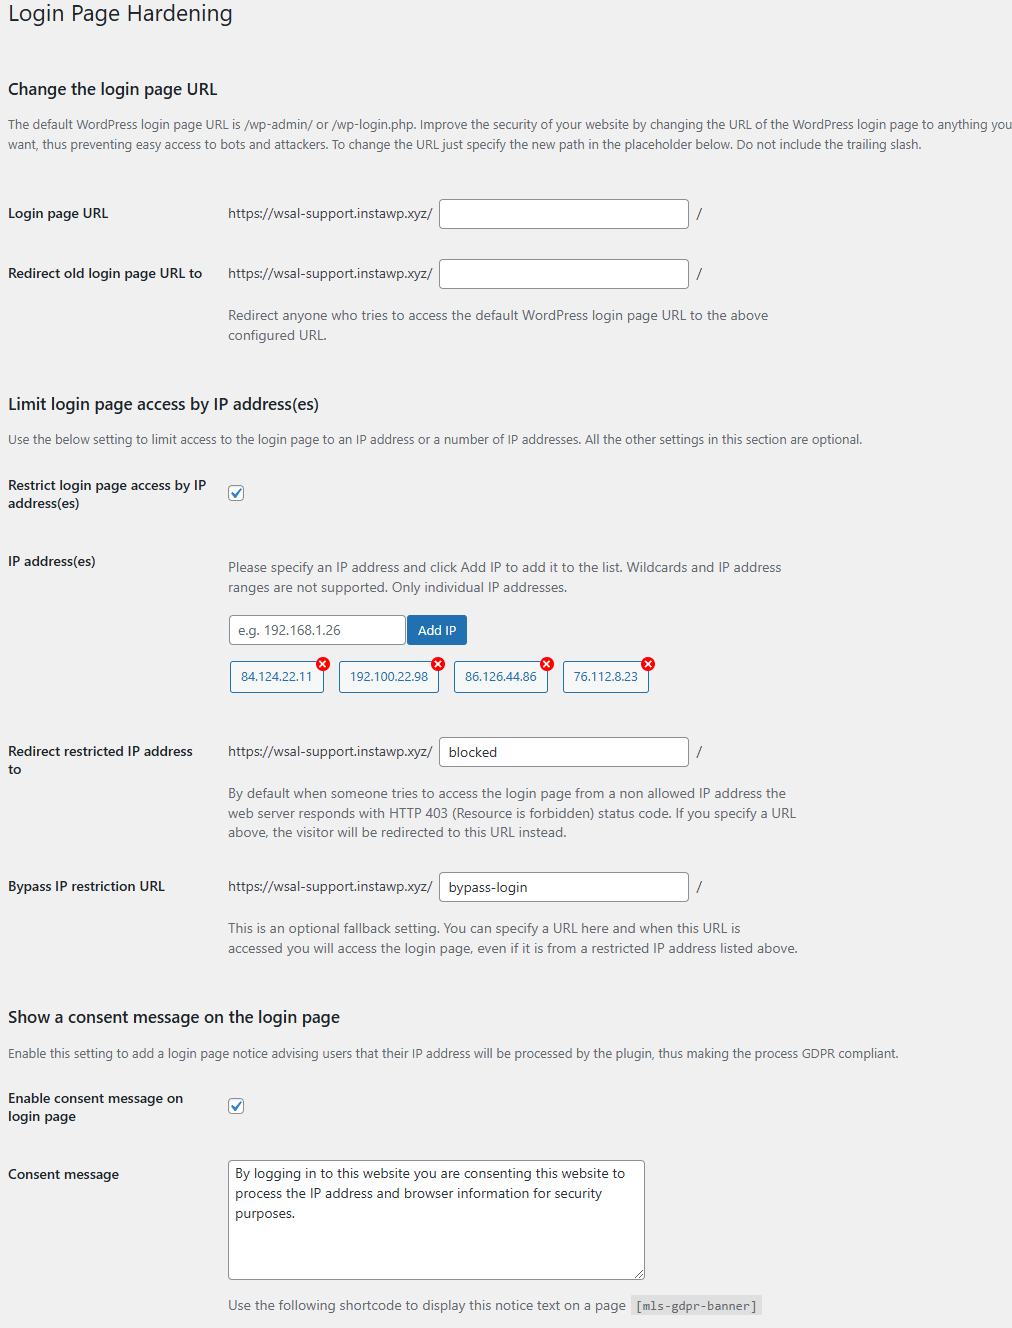
Eenvoudig beveiliging-door-obscuriteitstactieken inzetten en je WordPress loginpagina-URL wijzigen met een plugin! Het verbergen van de standaard loginpagina voor hackers maakt het moeilijker om te vinden, wat mogelijk brute force-aanvallen en andere ongeautoriseerde toegangspogingen vermindert. Nadat je de standaard wp-beheer URL hebt gewijzigd, kun je een 404 instellen voor de oude loginpagina of deze omleiden naar een pagina van je keuze.
Beperk toegang tot de login pagina op basis van IP-adres(sen)
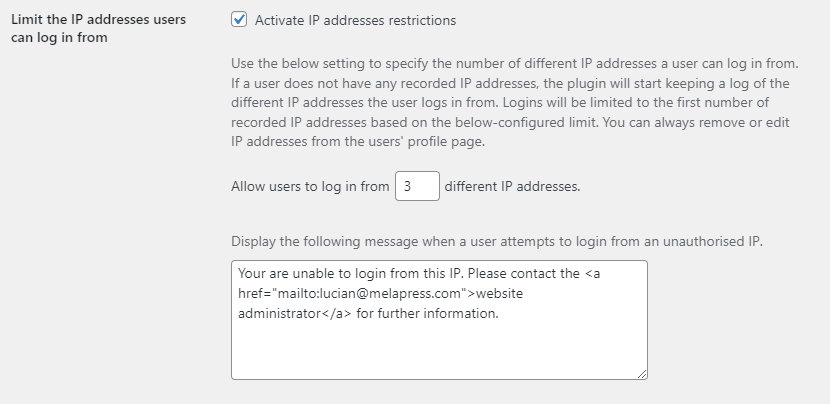
Beperk de toegang tot de WordPress login pagina op IP-adres(sen) voor extra beveiliging.
AVG/GDPR login pagina toestemmingsbericht
Voldoe eenvoudig aan de AVG/GDPR vereisten door een AVG/GDPR toestemmingsbericht toe te voegen aan de login pagina. Dit is vereist voor AVG/GDPR en PCI DSS naleving, waardoor je WordPress site login pagina in overeenstemming is.
Noodwachtwoord reset
Verdacht gedrag ontdekt? Reset alle wachtwoorden van gebruikers met slechts één klik en herwin direct de controle.
Upgrade naar Melapress Login Security Premium en krijg nog meer voordelen.
De premium editie van Melapress Login Security wordt geleverd met nog meer functies, waarmee je de login beveiliging van je WordPress site naar een hoger niveau kunt tillen. Schakel inactieve WordPress gebruikersaccounts uit en dwing wachtwoorden te resetten zodra accounts zijn ontgrendeld. Inactieve accounts kunnen binnen één dashboard worden beheerd voor verhoogde efficiëntie en snellere reactietijden. Bovendien kun je accounts laten vergrendelen na een aantal mislukte inlogpogingen en de duur en methode van ontgrendeling aanpassen.
Premium functies lijst
- Everything included in the free edition
- Manually lock user accounts to immediately prevent login access for rarely used accounts or users on extended leave
- Voeg een extra beveiligingslaag toe met beveiligingsvragen gebruikers moeten beantwoorden wanneer ze gevoelige acties uitvoeren zoals wachtwoord resets en account ontgrendelingen
- Receive email alerts for unrecognized device logins, with the option to remotely terminate the session
- Control user session duration by extending or shortening session timeouts to balance security and convenience
- Integratie met één klik met plugins van derden zoals WooCommerce, LearnDash, MemberPress en vele anderen
- Automatisch WordPress gebruikers inactief maken na een instelbare periode van inactiviteit
- Apply Geo-blocking rules to allow or block login access based on specific countries
- Gebruikerslogin tot specifieke IP-adressen beperken, inclusief ondersteuning voor meerdere toegestane IP’s
- WordPress gebruiker login tijden beperken per dag en/of uren
- Limit login credentials to email address, username, or both
- Een AVG/GDPR toestemmingsbericht toevoegen aan de WordPress login pagina
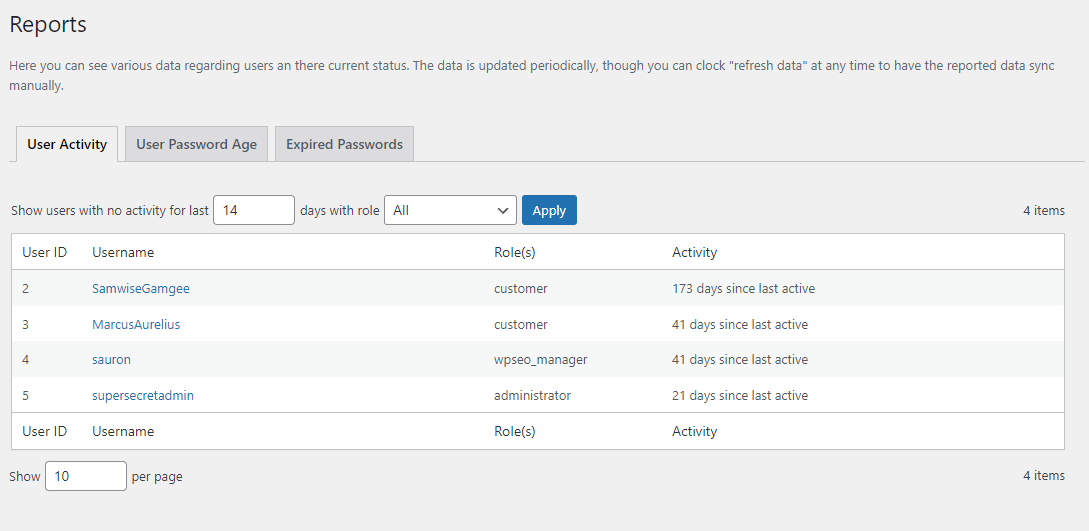
- View detailed user security reports, including last activity, password age, and expired passwords
- Receive weekly email summary reports covering password resets, password changes, user account lockouts, and more
Waarom je Melapress Login Security zou moeten gebruiken
Melapress Login Security is een WordPress plugin die vanaf de basis is opgebouwd om je te helpen de beveiliging van je gebruikersaccounts te verbeteren en je WordPress login te beveiligen. Geef login gegevens extra kracht voor maximale effectiviteit en maak een einde aan onbeperkte login pogingen, zwakke wachtwoorden en niet-actieve gebruikers. Stel regels in om je aanvalsoppervlak te beperken, zoals beperkingen voor login tijden, wijzig de WordPress login URL en nog veel meer.
Gratis en premium ondersteuning
Ondersteuning voor de gratis editie van Melapress Login Security is gratis op de WordPress ondersteuning forums. Premium wereldklasse ondersteuning via één-op-één e-mail is beschikbaar voor de Premium gebruikers – upgrade naar premium om te profiteren van prioriteitsondersteuning.
Voor andere vragen, feedback, of als je gewoon contact met ons wil opnemen, gebruik dan ons contactformulier.
ONDERHOUDEN & ONDERSTEUND DOOR MELAPRESS
Melapress bouwt hoogwaardige WordPress beveiliging & beheer plugins zoals WP 2FA, Melapress Role Editor, en WP Activity Log, de #1 door gebruikers beoordeelde activiteit log plugin voor WordPress.
Bezoek onze site om te zien hoe onze plugins je kunnen helpen bij het beter beheren en verbeteren van de beveiliging en beheer van je WordPress sites en gebruikers.
De plugin vanuit WordPress installeren
Een veilige WordPress login pagina behouden is eenvoudig met Melapress Login Security. Simpelweg:
- Vanuit je WordPress dashboard, navigeer naar Plugins > nieuwe toevoegen
- Zoek naar “Melapress Login Security ”
- Installeer & activeer Melapress Login Security vanaf je plugins pagina
Installeer de plugin handmatig (via bestand upload)
- Download de plugin uit de WordPress plugin repository
- Pak het zipbestand uit en upload de map naar de
/wp-content/plugins/folder - Activeer de Melapress Login Security plugin via de Plugins pagina in WordPress
Schermafbeeldingen
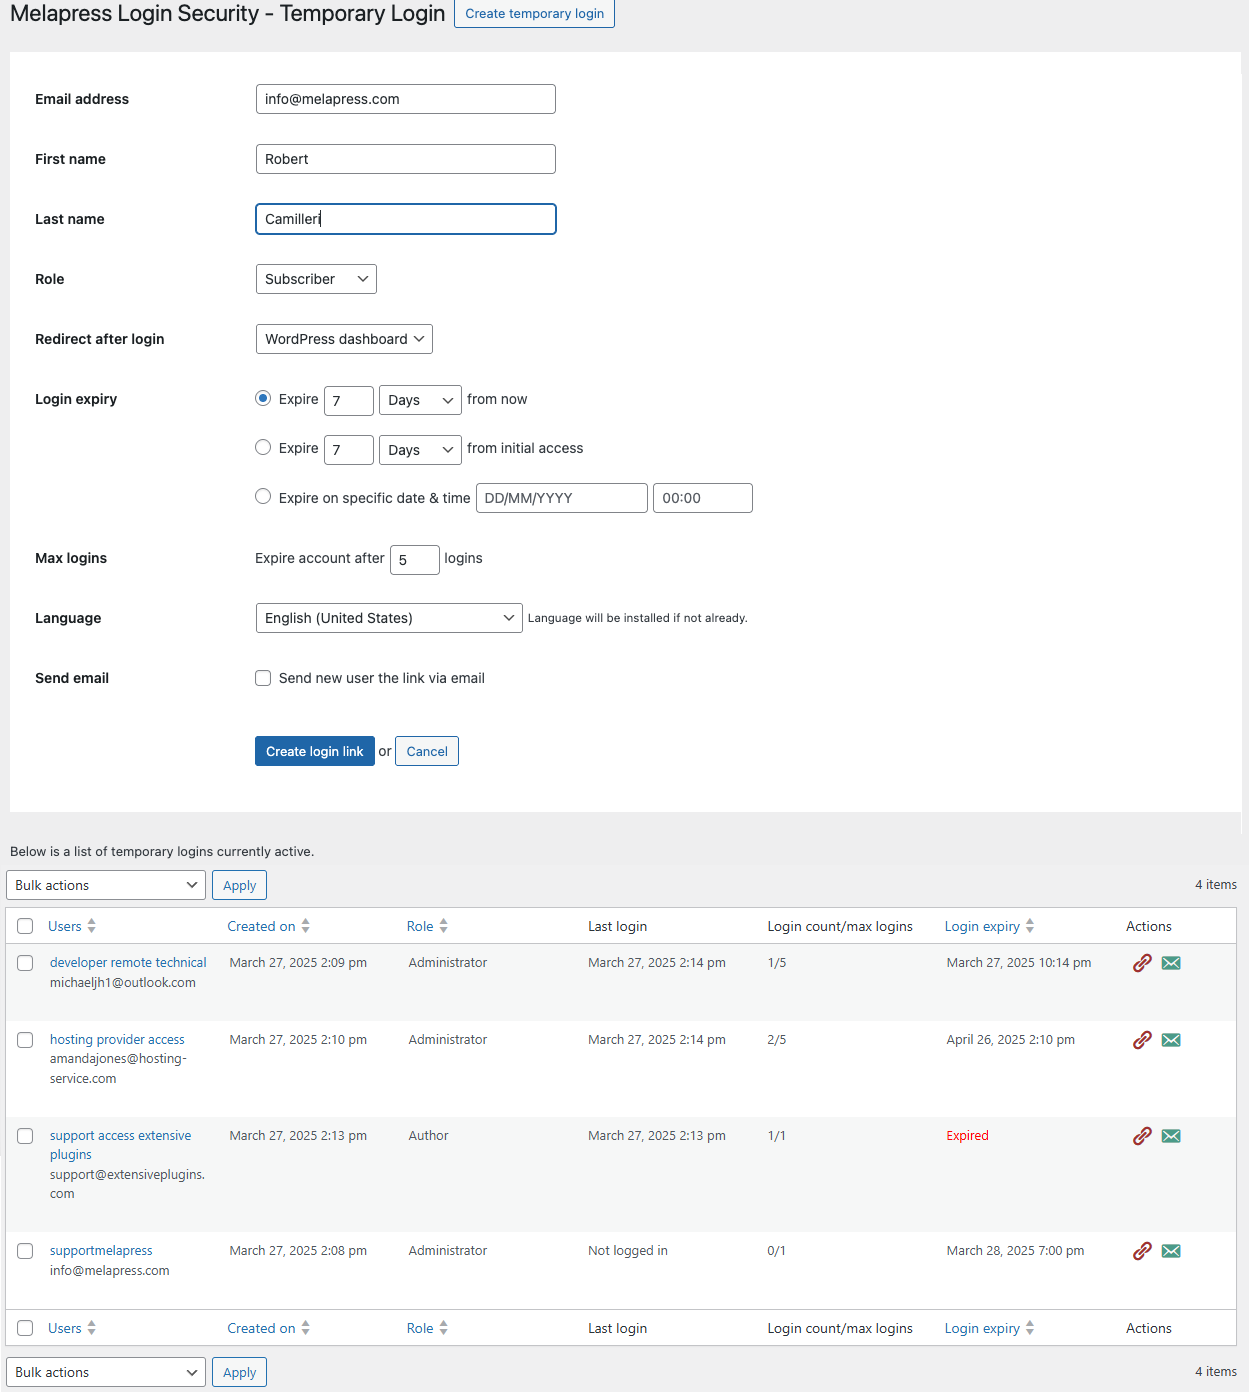
Maak eenvoudig tijdelijke veilige logins zonder wachtwoorden die automatisch verlopen na een specifieke periode of een aantal keer gebruik.
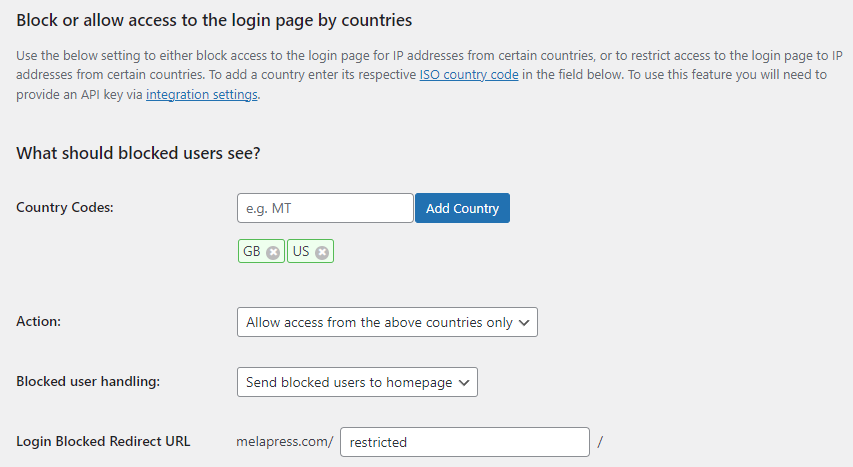
In de Premium editie kun je ook het verkeer naar de login pagina beperken op land of een aantal landen.
FAQ
Waar kan ik terecht voor verdere lectuur en documentatie?
Je kunt meer gedetailleerde informatie vinden over WordPress site beveiliging, wachtwoord beveiliging en gebruikersbeheer, beveiliging best practices, en nog veel meer in de aanbevolen lectuur hieronder gelinkt:
Is Melapress Login Security gratis?
Melapress Login Security is beschikbaar in zowel gratis als premium edities. De gratis editie zit boordevol beveiligingsmaatregelen om je WordPress login te beschermen, waaronder:
- Wachtwoordbeleid voor al je gebruikers
- Beperk login pogingen
- Wijzig login URL
- AVG/GDPR login pagina melding
De premium editie voegt functies toe zoals:
- Login tijden beperkingen
- Inactieve gebruikersbeleid
- IP-beperkingen
- Geo blokkering
- Een-klik integratie met WooCommerce, Memberpress, LearnDash en anderen
- en nog veel meer!
De gratis editie bevat alle basisfuncties zonder enige beperkingen om je WordPress login beveiliging te verbeteren. De premium editie voegt verschillende functies toe bovenop wat beschikbaar is in de gratis editie, waardoor je je WordPress login beveiliging nog verder kunt verbeteren.
Kan ik ondersteuning krijgen als ik vastloop?
Ondersteuning voor de gratis editie van de plugin wordt alleen verstrekt via de WordPress.org ondersteuningsforums. Je kunt ook onze ondersteuningspagina’s raadplegen voor alle technische en productdocumentatie.
Als je de Premium editie gebruikt, krijg je directe toegang tot ons ondersteuningsteam via een-op-een e-mailondersteuning.
Hoe beveiligt Melapress Login Security mijn site?
Melapress Login Security beveiligt verschillende aspecten van het WordPress login proces om de algehele beveiliging van je site te verhogen. Afhankelijk van welke editie je krijgt en welke beleidsregels je activeert, is de plugin flexibel genoeg om je in staat te stellen zo restrictief te zijn als je wilt.
Hoewel de plugin uitgebreid is, is het geen wondermiddel, en je moet nog steeds andere beveiligingsmaatregelen nemen, zoals het inschakelen van twee-factor authenticatie.
Hoe verbetert het beperken van inlogpogingen de beveiliging?
Brute force aanvallen vertrouwen op onbeperkte login pogingen om zoveel mogelijk gebruikersnaam- en wachtwoordcombinaties te proberen totdat ze de juiste combinatie vinden. Door inlogpogingen te beperken, stop je brute force aanvallen effectief door het ene ding te verwijderen waarop ze vertrouwen om je login pagina te kraken.
Hoe effectief is het wijzigen van de standaard WordPress login URL?
Het wijzigen van de URL van de login pagina is een beveiligingstechniek die bekend staat als security-by-obscurity. Het hele uitgangspunt is om middelen moeilijker vindbaar te maken – maar niet onmogelijk. Dit betekent dat het wijzigen van de wp-admin pagina URL een effectieve strategie kan zijn wanneer het wordt gecombineerd met andere technieken zoals het gebruik van sterke wachtwoorden en twee-factor authenticatie.
Ontvangt de plugin updates?
Melapress Login Security wordt actief ondersteund en ontvangt regelmatige updates. Raadpleeg de plugin changelog voor meer informatie over eerdere updates.
Hoe verwijder ik Melapress Login Security?
Je kunt Melapress Login Security net zo eenvoudig verwijderen als elke andere plugin. Log gewoon in op je WP beheer dashboard, navigeer naar Plugins > geïnstalleerde plugins, zoek Melapress Login Security, en klik vervolgens op Deactiveren en daarna op Verwijderen.
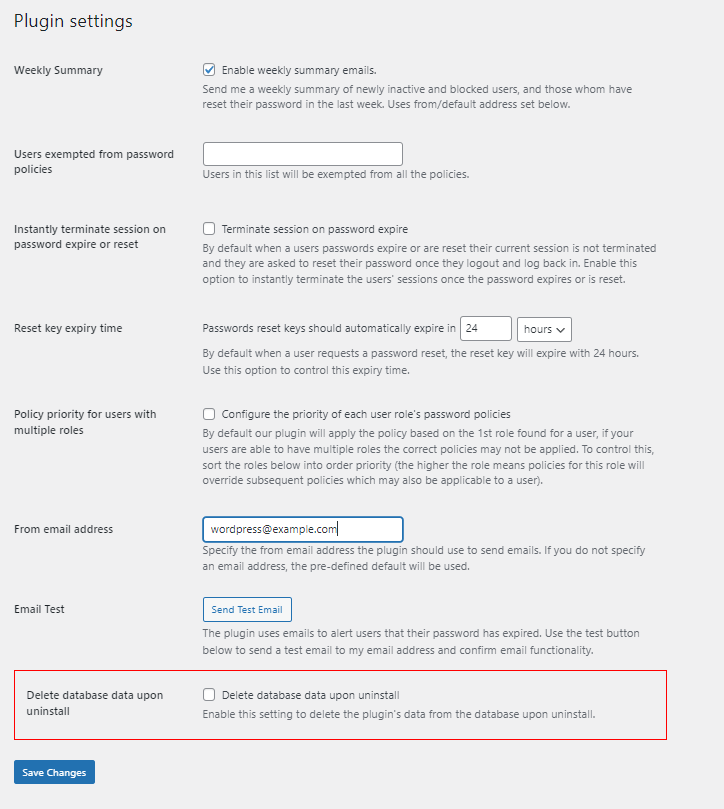
Om alle instellingen te verwijderen, navigeer naar Login Security > instellingen en schakel de Verwijder databasegegevens bij het verwijderen instelling in voordat je de plugin deactiveert en verwijdert.
Welke gegevens verzendt Melapress Login Security?
De gratis editie verzendt helemaal geen gegevens. De premium editie daarentegen verzendt alleen licentiegegevens naar onze server. Alle WordPress login beveiligingsinstellingen blijven in je WordPress database. Bovendien verzamelt de plugin geen gebruikersgegevens.
Hoe kan ik beveiligingsfouten rapporteren?
Je kunt beveiligingsfouten melden via het Patchstack Vulnerability Disclosure Program. Gebruik hiervoor dit formulier. Voor meer details, raadpleeg ons Melapress plugins beveiligingsprogramma.
Beoordelingen


Bijdragers & ontwikkelaars
“Melapress Login Security” is open source software. De volgende personen hebben bijgedragen aan deze plugin.
Bijdragers
“Melapress Login Security” is vertaald in 3 localen. Dank voor de vertalers voor hun bijdragen.
Vertaal “Melapress Login Security” in je eigen taal.
Interesse in ontwikkeling?
Bekijk de code, haal de SVN repository op, of abonneer je op het ontwikkellog via RSS.
Changelog
2.4.0 (2026-09-02)
Version 2.4.0 (2026-09-02) Feature and maintenance update
-
New features & functionality
- Added search and filtering options to the Locked Users table, including username, email, user ID, user role, and block reason.
- Added a new policy requiring users to enter their current password before setting a new one.
- Added a new policy, requiring users to answer their security questions before changing their own email address.
- Added Lock user and Unlock user actions to WordPress user profile pages for administrators.
- Added a two-factor authentication option that installs and activates the free WP 2FA plugin, or opens its settings when it is already installed.
- Added support for the new self-hosted licensing system while maintaining support for existing Freemius licences.
- Added a Premium email notification for new logins when the user already has an active session.
- Added a known devices list to the user profile page, allowing users to view the known devices associated with their account.
-
Functionality & plugin improvements
- Increased the minimum supported PHP version to 8.0.
- Split password, session, device, and login policies into separate groups that administrators can enable or disable independently.
- Improved unrecognized device detection by using a secure device cookie instead of the browser User-Agent.
- Added a Recognized device duration setting with options for 1 month, 3 months, 6 months, or 1 year.
- Centralized user lock handling so users can have only one active lock. The original lock reason is preserved, and one unlock action now clears the lock.
- Manual user locks now record when the lock was applied and show this value in the Locked since column.
- Improved the forced password reset process after unlocking an account. Users cannot create an authenticated session with their old password while a required reset is pending.
- Added email address columns to the Locked Users and Reports pages.
- The Expired Passwords report now shows the actual expiry date and time under the Password expired on column.
- Improved server-side validation for policy limits, login credential options, failed-login unlock options, IP addresses, redirect URLs, country codes, and login-page messages.
- Improved settings exports so licence credentials are not included in exported files.
- Updated plugin emails in Free and Premium to use a simpler plain-text layout without logos or background images. Free emails include a Melapress Login Security attribution link, which Premium users can customize.
- Improved direct file access protection, output escaping, and request verification following a WordPress Plugin Check review.
- Updated the Premium Features tab to distinguish between Premium and Enterprise functionality.
- Updated the plugin update notice and added a smaller Premium features banner.
- Other plugin notices are now hidden on Melapress Login Security admin pages to reduce distractions.
- Moved Account / Manage License to the last position in the plugin menu.
- Renamed Run Inactive Check Now to Refresh users lock status in Free and Premium.
- Improved the policy exclusions and Enterprise email formatting help text.
- The password expiry notification controls now show the full “send up to” text only when the setting is enabled.
- Removed the notice count badge from the plugin menu.
- Updated the deactivation feedback form to version 1.1.
- Removed the Ad link URL from the plugin details displayed on the WordPress Plugins page for non-Enterprise plans.
-
Oplossingen voor bugs
- Role-specific password policies are now correctly applied when creating users instead of falling back to the site-wide policy.
- The Do not enforce password policies for this role setting is now respected when creating users, changing passwords, editing profiles, and resetting passwords.
- Added missing separators between multiple password validation messages.
- Fixed an HTTP 500 error that could occur after password expiry when the reset email could not be sent. Expired users are now correctly directed through the required reset process.
- Fixed settings imports that could disable enabled password rules when boolean values were stored in the exported file.
- Fixed imports from older plugin versions deleting settings introduced in newer versions.
- Fixed incomplete imports of policy settings, email template customizations, HTML message content, and excluded users.
- Fixed password policies being disabled when importing settings exported from version 2.3.0.
- Fixed expiry notification periods being changed incorrectly when the notification and expiry periods used different time units.
- Fixed the weekly summary email day dropdown not matching stored values because of letter-case differences.
- Fixed Enterprise timed-login restrictions remaining active on days that were unchecked.
- Fixed incorrect inactivity durations and filtering on the Reports page.
- Fixed the User Password Age report showing last activity information instead of password age and returning incorrect results.
- Fixed a PHP warning and incorrect timed-unlock calculation when a failed login was submitted using an email address.
- Fixed a fatal PHP error on plugin admin pages when another plugin or theme used an anonymous callback for an admin notice.
- Fixed WordPress 7.x layout overlaps on the Locked Users and Reports pages.
- Fixed the editable Unknown username notice reverting to its default value after saving.
- Fixed a state where the Login Security Policies page could not be saved when the excluded special characters setting was enabled without a value.
- Fixed Enterprise IP restrictions treating limits containing zero incorrectly.
- Fixed the inactive-user control appearing without working functionality in the Free edition.
- Fixed device policy labels that could move the browser to the bottom of the page or respond inconsistently when clicked.
- Fixed out-of-range numeric policy values being accepted when settings were submitted outside the browser validation.
- Fixed an administrator email being sent after terminating an unrecognized-device session when that notification was disabled.
- Fixed the Do not auto-generate a new password on reset option remaining enabled after it was unchecked.
- Fixed disabled user-unlock and multiple-session emails continuing to be sent.
- Fixed the manual inactive-user check returning incorrect feedback and logging an undefined variable warning.
- Fixed a fatal PHP error on PHP 8 when a custom login URL was configured.
- Fixed a fatal PHP error during password reset when password recycle policies were disabled and the password history value was empty or non-numeric.
- Fixed later lock policies overwriting the original reason for an existing manual, inactivity, or failed-login lock.
Raadpleeg de volledige plugin changelog voor meer gedetailleerde informatie over wat nieuw, verbeterd en opgelost was in eerdere versie updates van Melapress Login Security.